Workstation Logo
产品
AI 实验室OpenAI代理Claude 代理Grok BotWorkstation CRM (WSL CRM)营销全部产品
AI 解决方案
AI 工作站AI SME Packages私有 AIGPU 集群边缘 AI企业 AI 实验室按行业分类的 AI
服务
Platform ModernisationDigital EngineeringData Foundations & AIAutonomous OperationsAI 咨询DevOps 自动化网络安全软件开发智能体构建MLOps 搭建
关于我们
合作伙伴客户案例
文章
文档
WSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7
博客
联系我们Login
Workstation

面向现代企业的 AI 工作站、AI 多智能体软件、GPU 基础设施和智能代理解决方案。

联系我们

AI 解决方案

AI 工作站AI SME Packages私有 AIGPU 集群边缘 AI企业 AI 实验室按行业分类的 AI

产品

全部产品WSL CRM 与 ERP营销OpenAI代理WSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7

公司

关于我们为什么选择Workstation合作伙伴客户案例价格联系

资源

文章文档博客搜索网站地图
英国办公室
77-79 Marlowes, Hemel Hempstead HP1 1LF路线指引 — 从 M25 外环伦敦 20 号出口驶出公司编号: 11641870周一至周五:上午 9:00 - 下午 6:00 GMT
+44 7515 356 146
比利时办公室
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683周一至周五:上午 9:00 - 下午 6:00 CET
+32 492 45 67 46
印度办公室
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI。保留所有权利。

隐私Cookie服务条款网站地图

Loading blog...

Home / Blog
AIAI AgentsSecurityLLMDevOps

How to Deploy Secure AI Agents in Healthcare

Give agents the right access for appointments, billing and clinical support — with guardrails that keep PHI and payments out of the model

Balinder Walia2026年9月17日2 min read

AI agents can book appointments, take payments and support clinical work. Healthcare teams should give them the right access — and no more. Companion deep dive: long article.
How to deploy secure AI agents in healthcare

Bottom line. Do not ask whether the AI is “safe enough” to see all PHI. Ask what access the agent needs to finish the patient’s request — then keep everything else on fixed, rule-based paths with audit trails that do not copy more sensitive data.

Healthcare teams are moving past AI pilots. Agents can work out what a patient wants, pick a tool, connect to systems and take action: appointments, billing questions, payments and clinical support. That creates a new security problem. Normal software follows a fixed path. An agent does not — the path changes with the conversation. Near Protected Health Information (PHI) or payment data, the key question is least privilege, not model trust.

Three ideas for healthcare leaders
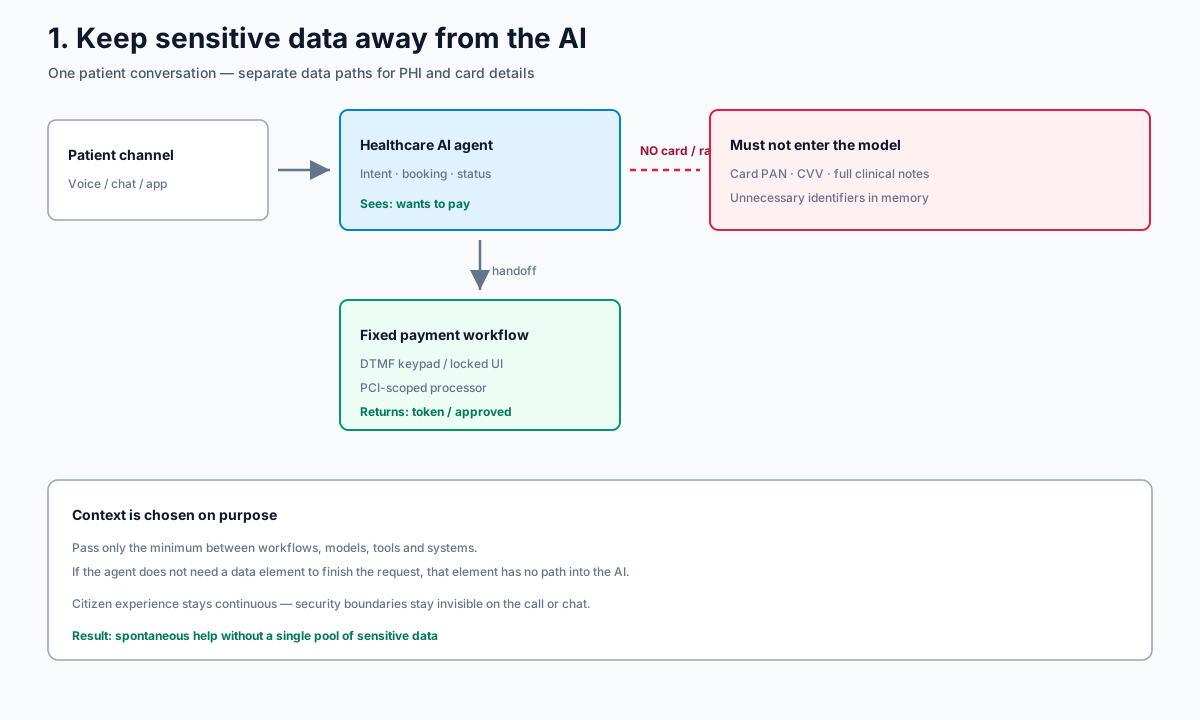
Keep sensitive data away from the AI agent

  1. Keep sensitive data away from the AI. On a bill-pay call, the agent needs intent and payment status — not the card number. Use DTMF or a locked digital payment flow; return only a token or “approved”. Context must be chosen on purpose, not passed by default.
  2. Do not use the AI as your security guard. Let the model understand language. Let fixed controls decide login, permissions and high-risk actions.
  3. Track what the agent did, not just what it said. Audit agent, workflow, tools, permission decisions, boundary crossings and results — without dumping PHI into logs and analytics.
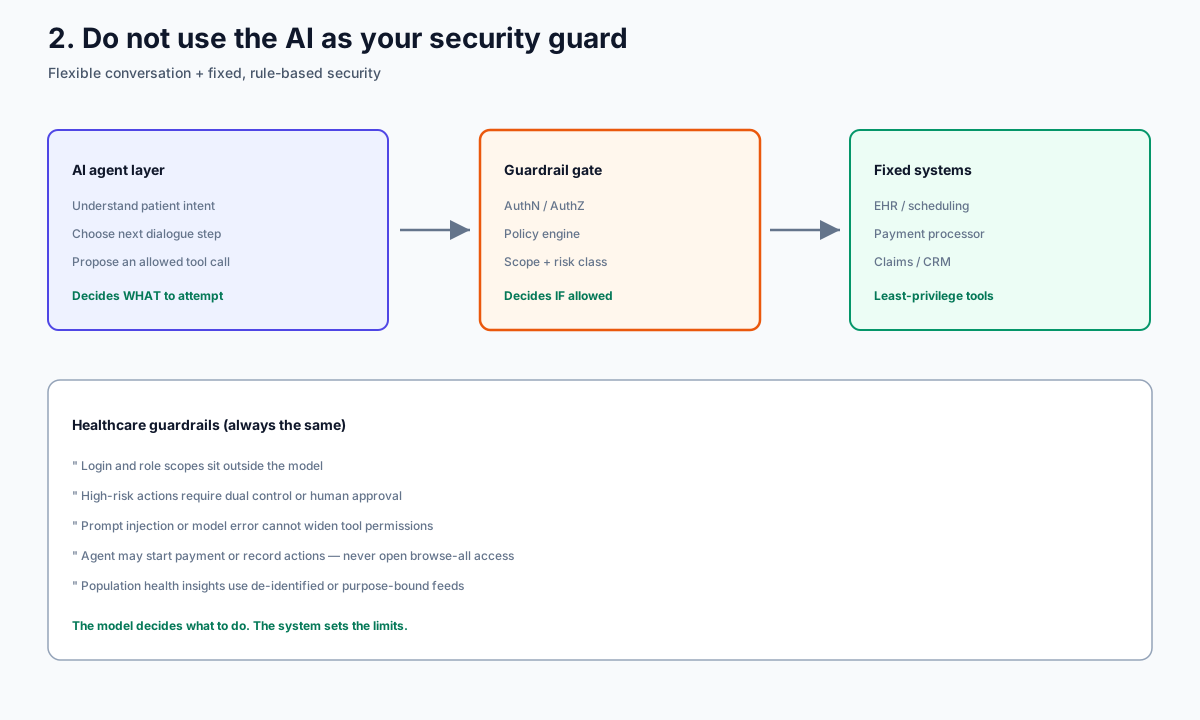
AI decides intent; system enforces healthcare guardrails

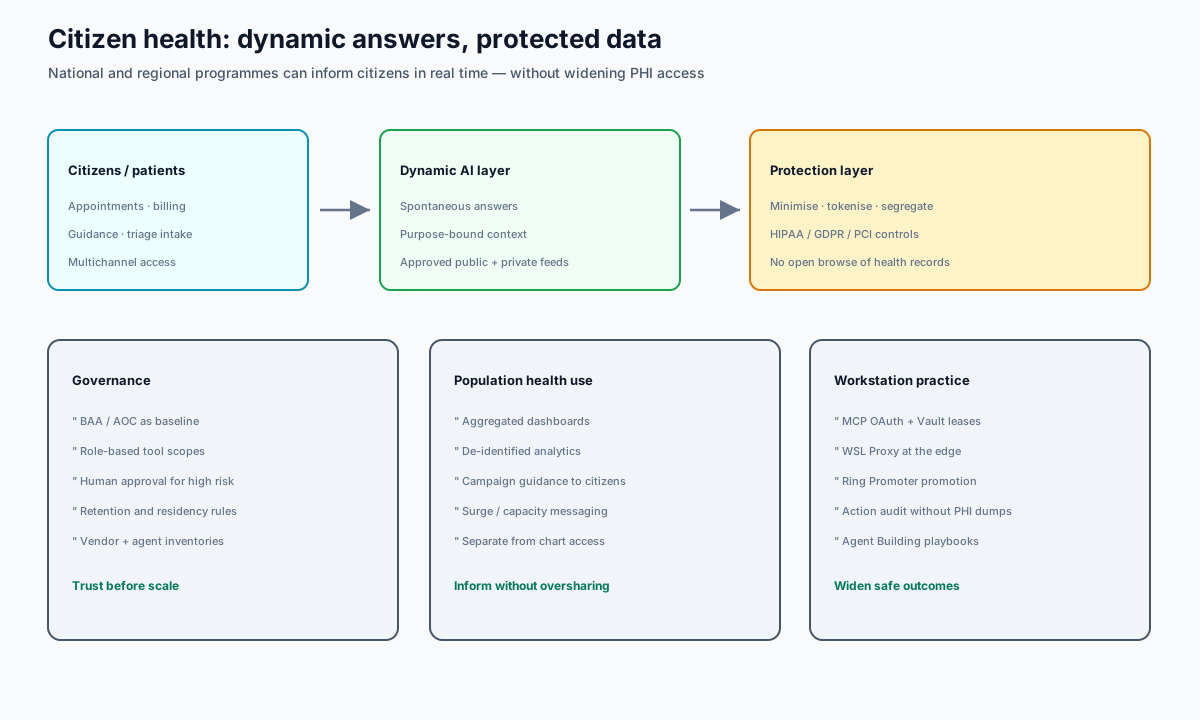
Citizen health dynamic answers with protected data

For national and regional programmes, citizens still need spontaneous, dynamic answers — appointments, guidance, capacity messaging — while charts and payment data stay behind purpose-bound feeds, tokenisation and governance. A BAA (HIPAA) and AOC (PCI DSS) are starting points, not the whole design.

Workstation practice. Pair flexible agents with MCP OAuth, Vault leases, edge controls (WSL Proxy), and promotion discipline (Ring Promoter). See also agentic security and AI Healthcare.

Read the full technical brief · Talk to Workstation