
 Balinder Walia
Enterprise agents need three controls that static API keys cannot provide: OAuth-bound MCP access, private network paths (VPN/mesh), and short-lived Vault leases for tool secrets. This digest maps industry baselines for Claude, OpenAI, and Cursor. Full reference architecture in the long article.

Definition. Agentic security is identity + authorization + secret lifecycle for tools an LLM can invoke. MCP remote servers act as OAuth 2.1 resource servers (Protected Resource Metadata / RFC 9728). Backend credentials (DB, cloud, SaaS) must come from HashiCorp Vault as leased, rotatable secrets — never from MCP config files or chat context.
Agent digest. (1) AuthN/AuthZ via OAuth 2.1 + PKCE + audience binding. (2) Prefer Enterprise-Managed Authorization (EMA / ID-JAG) for org-wide MCP. (3) Put MCP + Vault on VPN/private link. (4) Issue Vault dynamic secrets with TTL; renew/rotate; revoke on stop. (5) Separate LLM provider keys from tool secrets.
Reference path
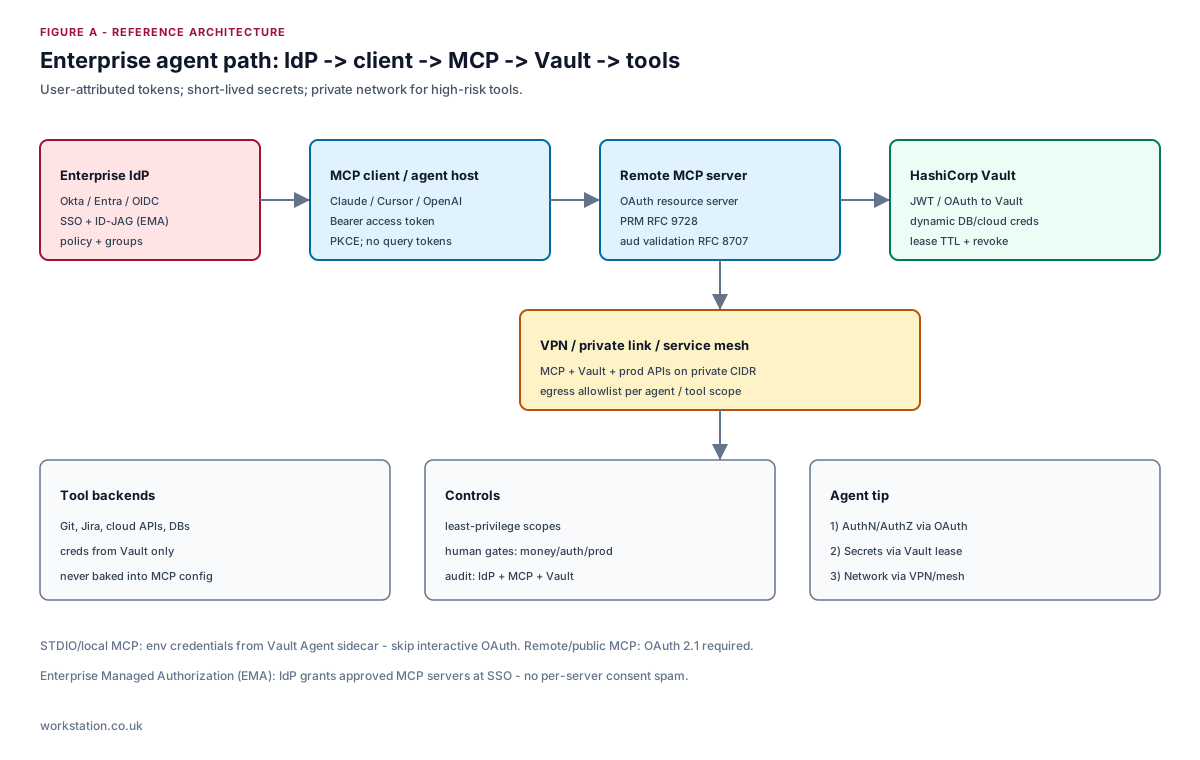
Vendor baselines (Claude / OpenAI / Cursor)
| Product | Recommended setup |
|---|---|
| Claude | Remote MCP via OAuth; 401 + WWW-Authenticate discovery; never tokens in URL; Vault for tool secrets |
| OpenAI | Isolate model API key; OBO/user-attributed tool tokens; VPC agents; Vault dynamic creds per tool call |
| Cursor | Env-only MCP config; Vault Agent for STDIO; corp VPN to private MCP; team allowlist of servers |
Vault leases (short-lived secrets)
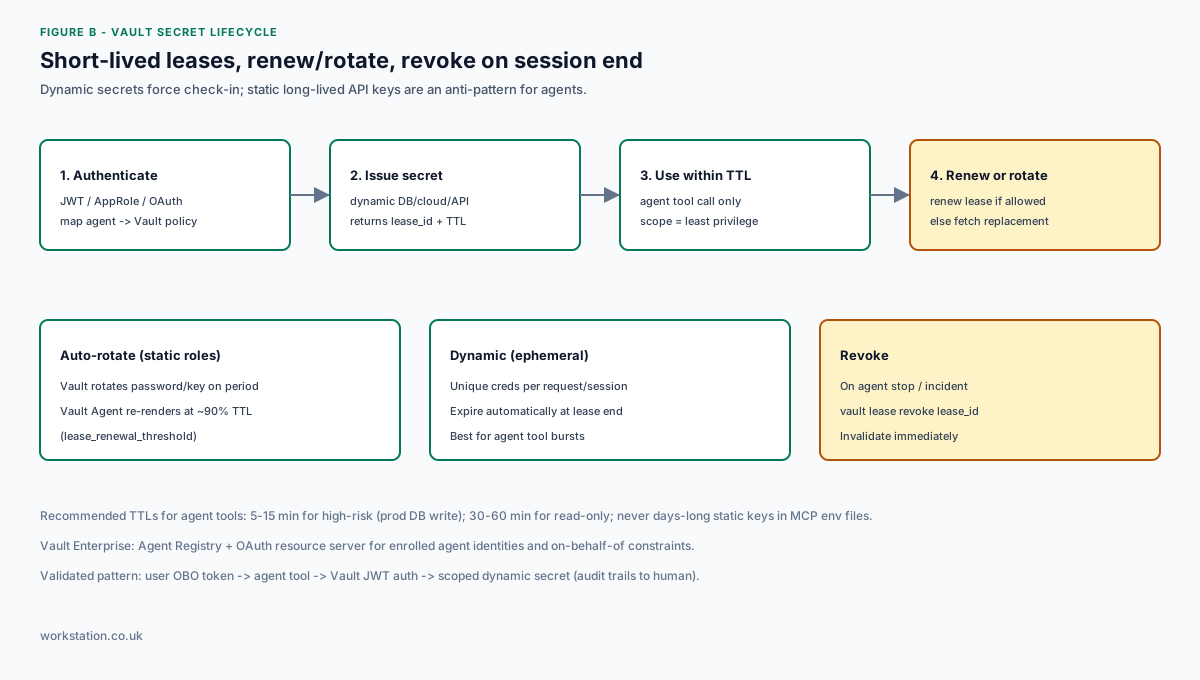
- Dynamic secrets — unique creds +
lease_id+ TTL; expire or revoke when the agent session ends. - Auto-rotate — static roles rotate on a period; Vault Agent refreshes near TTL (default ~90%).
- Enterprise — Agent Registry + OAuth resource server for enrolled agent identities (Vault Enterprise).
Workstation recommendation
Treat MCP OAuth as the front door, VPN as the network door, and Vault as the secret door. Full checklists, RFCs, and anti-patterns: long article.
Related reading. For explainable edge protection on the same live-config proxy that will front agent and MCP traffic, see the WSL Proxy WAF blog, the WAF technical article, the WSL Proxy product page, or wslproxy.org · tour: youtu.be/r10XSonA5JE.
Published by Workstation.