Long-form technical companion to the compliance blog. How WSL Vault makes secret management a breeze for operators while enforcing cryptographic tenant isolation, dual-control shared access, MFA, dynamic leases, and active/active multi-region HA. Product: Workstation WSL Vault · wslvault.org · GitHub.
Presentation (~20 min) — youtu.be/O6q3_H0k2M8 · Silent tour: wslvault.org/#tour
1. Why shared root power fails audits
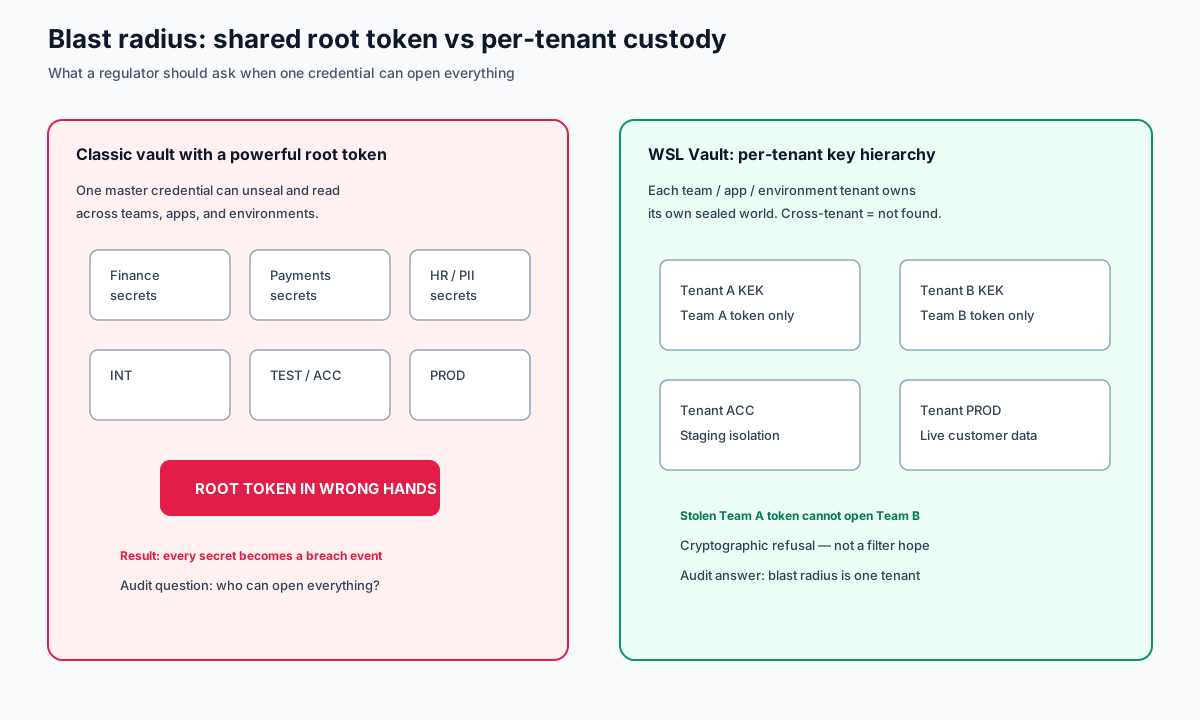
In many HashiCorp Vault deployments, a root token (or equivalent highly privileged unseal/admin path) remains the organisational backstop. That credential’s blast radius is the entire secrets graph: every namespace, every environment, every team’s API keys and database passwords. If it lands in the wrong hands, you do not have an incident ticket — you have a breach narrative.
WSL Vault’s answer is structural: identity is a signed, per-tenant token; material is sealed under a tenant KEK; cross-tenant requests fail closed at the crypto layer. Root custody, when needed for unseal, can be Shamir-split so no single operator holds the whole key.
2. Envelope encryption — the reason isolation is real
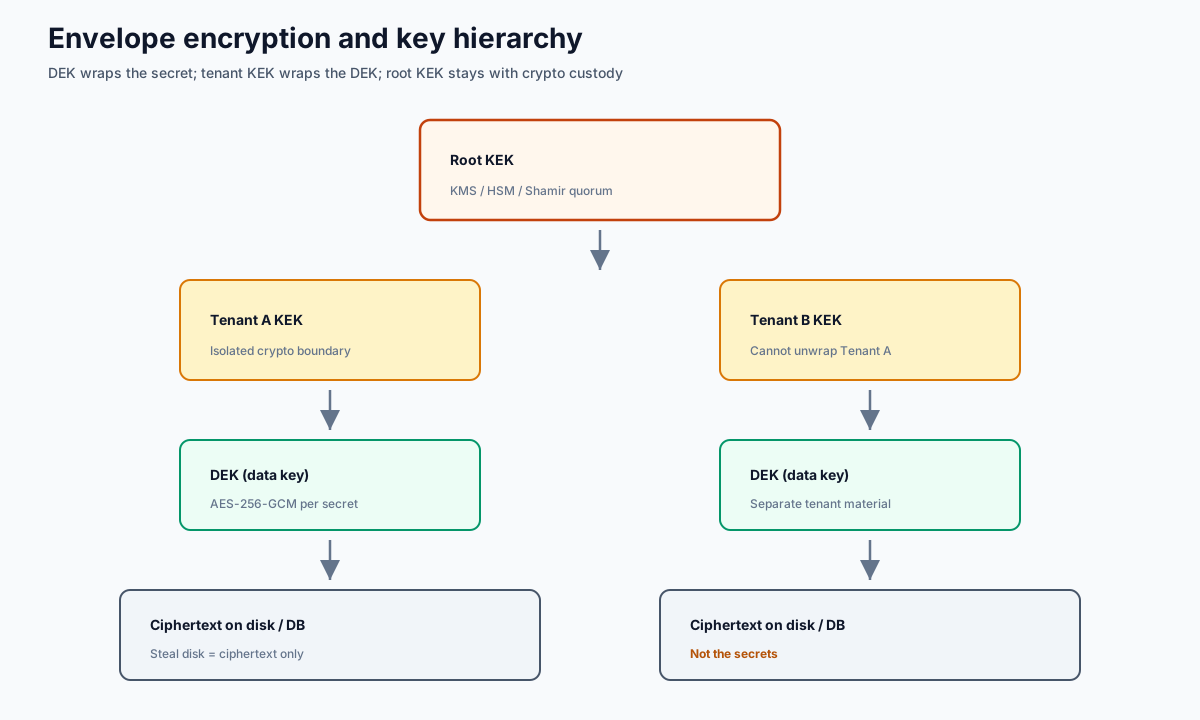
Each secret is sealed with a data encryption key (DEK). The DEK is wrapped under a tenant KEK. Tenant KEKs are wrapped under a root KEK held by the crypto service (KMS, HSM, or Shamir quorum). AES-256-GCM provides authenticated encryption. A database dump yields ciphertext wrapped under keys the database never sees.
That is why “steal the server” does not equal “steal the secrets” — and why Team A’s token cannot unwrap Team B’s DEKs even if an upper layer mislabels a path.
3. Tenants for apps, teams, and environments
Model the organisation the way auditors already think:
- App tenants — Shop vs OpsAPI vs edge proxies each keep separate sealed material.
- Team tenants — Platform, payments, data science never share unwrap rights by accident.
- Environment tenants — INT / TEST / ACC / PROD as separate crypto worlds so a staging token cannot open production.
Isolation is not a WHERE clause. A cross-tenant read returns not found. That cryptographic refusal is what you show in a control description.
4. Ceremony workflow — oath and dual-tenant control
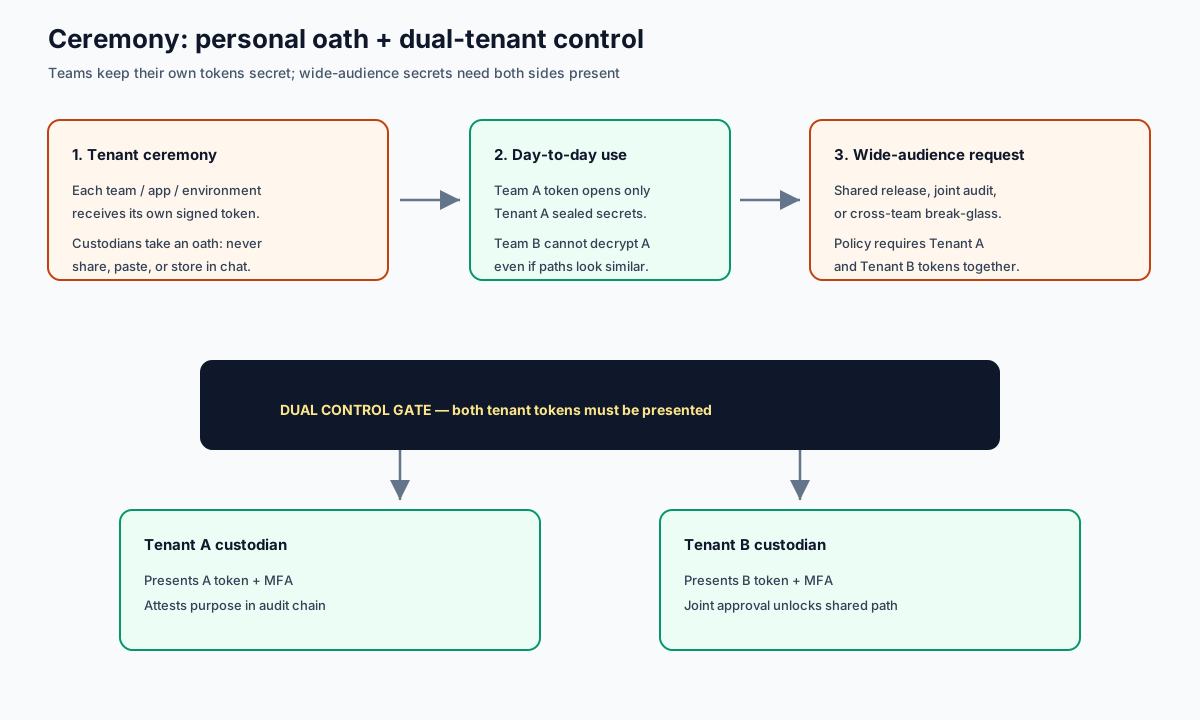
- Issue — At ceremony close, each tenant custodian receives a signed per-tenant token (and MFA enrolment).
- Oath — Custodians accept personal responsibility: never share the token, never store it in chat or git, rotate on departure.
- Day-to-day — Team A operates only inside Tenant A. Sprawl drops because the vault is the fastest place to put a secret.
- Wide audience / shared path — For secrets that must be obtained across tenants (joint release, shared break-glass, dual approval), policy requires both Tenant A and Tenant B tokens (plus MFA). Neither side alone succeeds.
- Audit — Both presentations and the stated purpose land on the per-tenant hash chain.
That dual-control gate is how you translate zero trust into an operating procedure regulators recognise.
5. Making secrets a breeze — engines and workflows
Feature tour (aligned with wslvault.org/#features):
| Surface | Operator experience | Security property |
|---|---|---|
| KV v2 | Versioned put/get, check-and-set, soft-delete/destroy | Sealed before disk under tenant hierarchy |
| Transit | Encrypt / decrypt / sign / verify in one call | Plaintext keys never leave the vault |
| PKI | Private CA, roles, short-lived certs | CA keys envelope-encrypted |
| Leases | Issue, renew, list, revoke | Revoke stops use immediately |
| Identity + MFA | TOTP, recovery codes, OIDC/LDAP/mTLS/workload | Signed per-tenant token — never a trusted header alone |
$ wslvault login --key wslv_…
✓ authenticated as tenant payments  region=manchester  mfa=ok

$ wslvault kv put prod/db/creds password=••••
✓ sealed with dek 01a0…93a7  version=1

$ wslvault kv get prod/db/creds --region london
# same secret, peer region decrypt
password = ••••   replication_lag=14ms

$ wslvault lease revoke lease_…
✓ credential dead — not a soft flag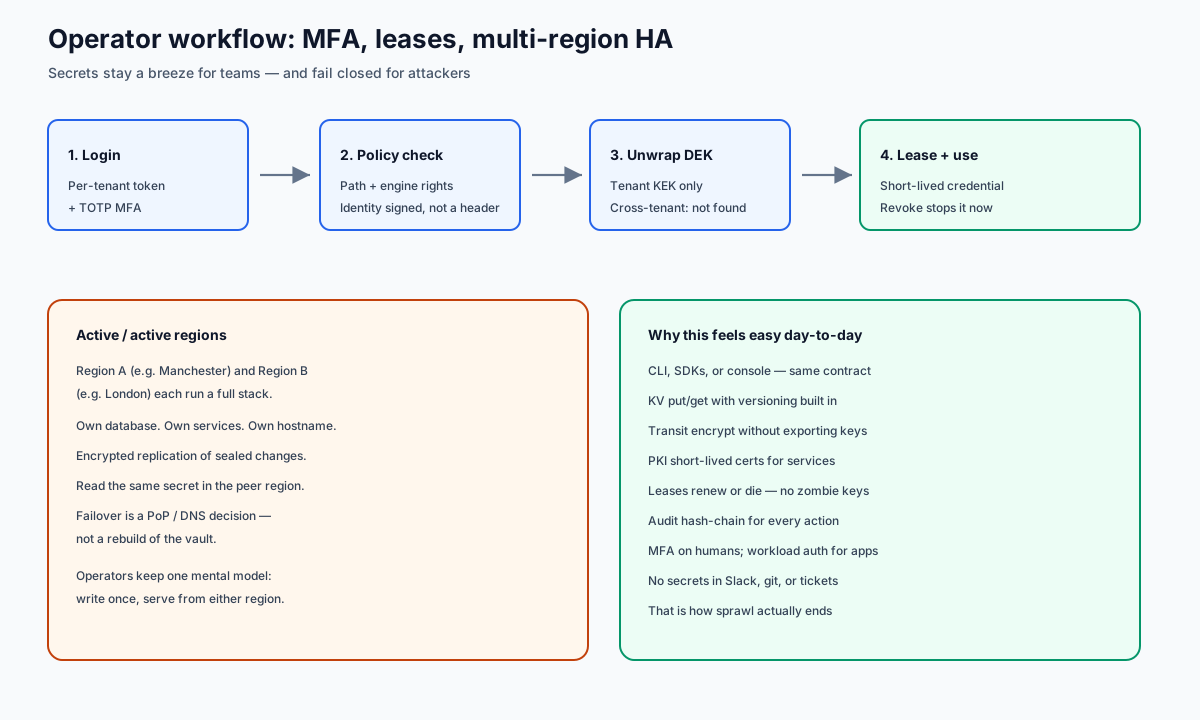
6. MFA and identity detail
Humans enrol self-service TOTP with recovery codes. API keys and JWTs sit under fine-grained policies. Workloads authenticate with mTLS or cloud-workload patterns so apps never borrow a human root. Identity always resolves to a tenant-scoped principal before any unwrap.
That combination — MFA for people, short leases for machines — is what keeps “convenient” from becoming “copied into a wiki.”
7. Multi-region HA without a shared live database
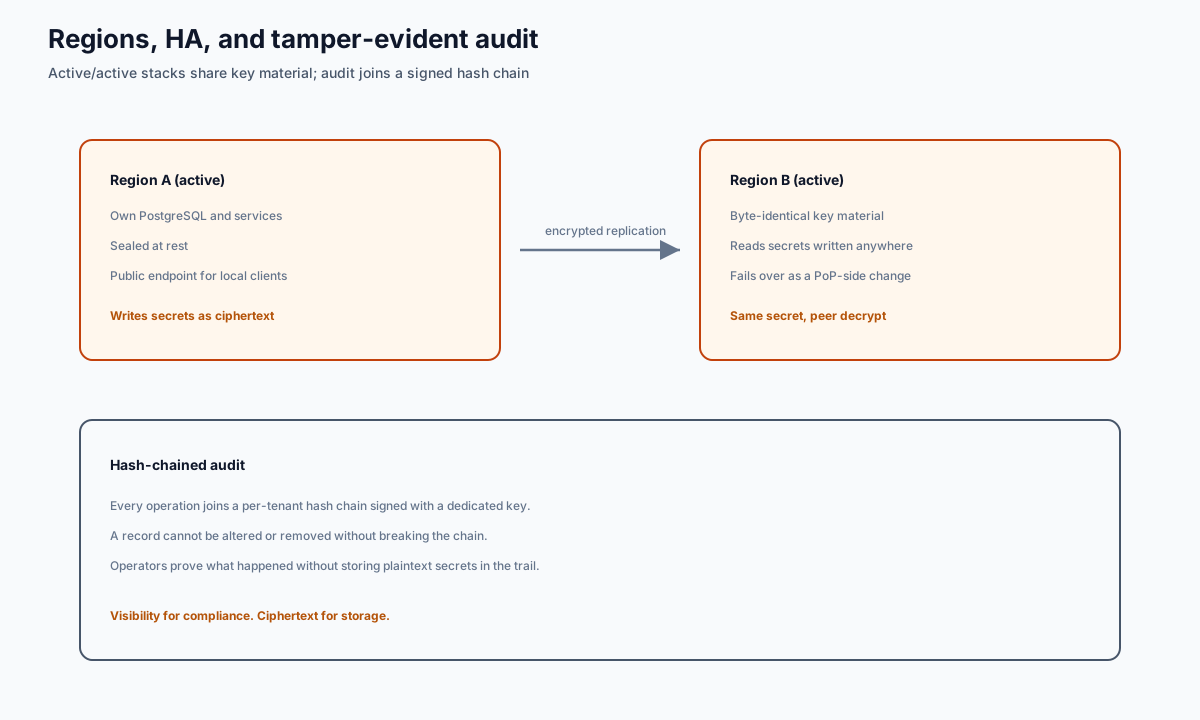
Each region is a complete stack: own PostgreSQL, own services, own public hostname. Regions share key material, not one hot database. Agents pull encrypted changes over the public edge. Clients read the same sealed secret from the peer with low replication lag. Failover is a PoP / traffic decision — operators do not rebuild custody under pressure.
Every operation joins a per-tenant signed hash chain. Records cannot be silently altered without breaking the chain — the evidence pack auditors ask for.
8. Deploy path — Kubernetes, Helm, GitOps
Ship with the Helm chart and operator; scrape Prometheus; drive from Argo CD / GitOps. Clients: CLI plus Go, Python, Rust, TypeScript SDKs, and an MCP server for agent tooling. Getting started: GETTING-STARTED.md.
9. Guided tours (videos and site)
| Tour | Where | What you see |
|---|---|---|
| Silent console (~2 min) | wslvault.org/#tour | Tenants, KV, transit, MFA, regions, audit |
| Features | #features | Engines behind one API |
| Architecture | #architecture | Active/active region mesh + CLI demo |
| Security model | #security | Audit, Shamir, tenant isolation, no plaintext |
| Full presentation | youtu.be/O6q3_H0k2M8 | ~20 min deep walkthrough |
Presentation chapters (YouTube)
| Time | Topic |
|---|---|
| 0:00 | Why this matters (steal the server) |
| 1:30 | What WSLVault is |
| 3:00 | Envelope encryption and key hierarchy |
| 5:30 | Multi-tenancy that actually isolates |
| 8:00 | Console walkthrough (secrets, transit, PKI) |
| 11:00 | Identity, policies, leases and MFA |
| 14:00 | Regions, HA and audit |
| 17:00 | Deploy on Kubernetes |
| 19:00 | Where to go next |
10. Related Workstation content
- Compliance blog (this article’s companion)
- Intro blog · Intro technical brief
- AI agents blog · AI agents article
- Product page · wslvault.org · GitHub
Published by Workstation — secrets custody you can explain to a regulator and still enjoy as an engineer.