Workstation Logo
ผลิตภัณฑ์
AI LabsOpenAI AgentsClaude AgentsGrok BotWorkstation CRM (WSL CRM)การตลาดผลิตภัณฑ์ทั้งหมด
โซลูชัน AI
เวิร์กสเตชัน AIAI SME PackagesAI ส่วนตัวคลัสเตอร์ GPUEdge AIแล็บ AI องค์กรAI ตามอุตสาหกรรม
บริการ
Platform ModernisationDigital EngineeringData Foundations & AIAutonomous Operationsที่ปรึกษา AIระบบอัตโนมัติ DevOpsความมั่นคงปลอดภัยไซเบอร์การพัฒนาซอฟต์แวร์การสร้างเอเจนต์การตั้งค่า MLOps
เกี่ยวกับเรา
พาร์ทเนอร์เรื่องราวลูกค้า
บทความ
เอกสาร
WSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7
บล็อก
ติดต่อเราLogin
Workstation

เวิร์กสเตชัน AI ซอฟต์แวร์มัลติเอเจนต์ AI โครงสร้างพื้นฐาน GPU และโซลูชันเอเจนต์อัจฉริยะสำหรับธุรกิจยุคใหม่

ติดต่อเรา

โซลูชัน AI

เวิร์กสเตชัน AIAI SME PackagesAI ส่วนตัวคลัสเตอร์ GPUEdge AIแล็บ AI องค์กรAI ตามอุตสาหกรรม

ผลิตภัณฑ์

ผลิตภัณฑ์ทั้งหมดWSL CRM และ ERPการตลาดOpenAI AgentsWSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7

บริษัท

เกี่ยวกับเราทำไมต้อง Workstationพาร์ทเนอร์เรื่องราวลูกค้าราคาติดต่อ

แหล่งข้อมูล

บทความเอกสารประกอบบล็อกค้นหาแผนผังเว็บไซต์
สำนักงานสหราชอาณาจักร
77-79 Marlowes, Hemel Hempstead HP1 1LFเส้นทาง - ออกทางแยกที่ 20 จาก M25 Outer Londonเลขทะเบียนบริษัท: 11641870จ. - ศ.: 9:00 - 18:00 น. GMT
+44 7515 356 146
สำนักงานเบลเยียม
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683จ. - ศ.: 9:00 - 18:00 น. CET
+32 492 45 67 46
สำนักงานอินเดีย
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI สงวนลิขสิทธิ์

ความเป็นส่วนตัวคุกกี้ข้อกำหนดการให้บริการแผนผังเว็บไซต์

Loading blog...

Home / Blog
DevOpsSecuritySREKubernetesAI

WSLVault: Steal the Server. Not the Secrets.

Open-source secrets manager with envelope encryption, true multi-tenancy, KV/transit/PKI/leases, multi-region HA, and hash-chained audit

Balinder Walia22 กันยายน 25691 min read

Steal the server. Not the secrets. WSLVault is an open-source, self-hosted secrets manager built on AES-256-GCM envelope encryption and a per-tenant key hierarchy. This intro covers what it is, why the model matters, and how you drive it from console, CLI, or SDKs. Deep dive: long article · Product: /wsl-vault.

WSLVault — steal the server, not the secrets

Watch on YouTube (~20 min)

Bottom line. A stolen disk, database dump, or compromised host should leave attackers with ciphertext they cannot open. WSLVault seals every secret before storage — DEK → tenant KEK → root KEK — so multi-tenancy is cryptographic, not cosmetic.

WSLVault is built for operators who want Vault-compatible workflows without plaintext at rest: Rust services, Helm/GitOps on Kubernetes, CLI plus Go/Python/Rust/TypeScript SDKs, and a steel/brass web console.

What you will learn

  • True multi-tenancy — Team A cannot decrypt Team B (cryptographic refusal, not “oops”)
  • Envelope encryption — DEK → tenant KEK → root KEK (KMS / HSM / Shamir)
  • Engines — KV secrets, transit encryption, PKI, dynamic leases, MFA
  • Operations — Active/active multi-region replication and tamper-evident, hash-chained audit
  • Why it matters — Steal the disk ≠ steal the secrets
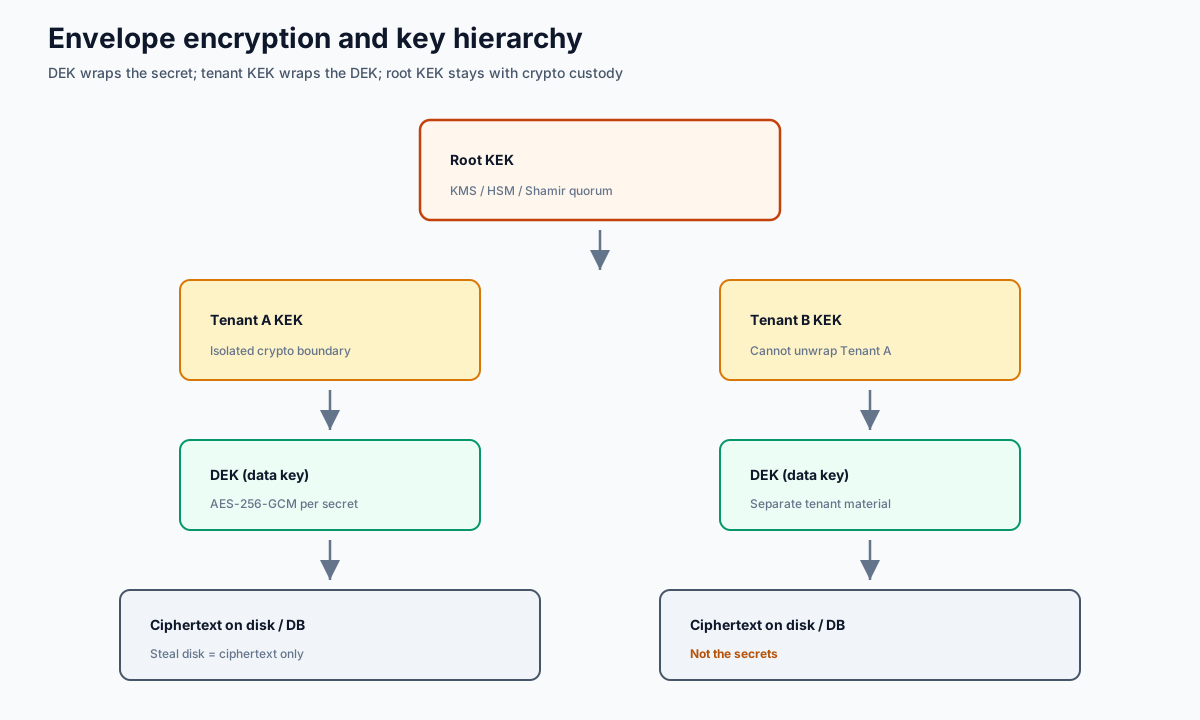
WSLVault envelope encryption key hierarchy

Links

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Docs: docs/
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault

Read the full technical brief · Open the WSL Vault tools page