Workstation ब्लॉग
Security
Security टैग वाली पोस्ट।
Agentic AI in Production: Permissions, Approval Gates, Traces and Evals
A practical playbook for running AI agents in production: classify every tool by side effect, gate mutations behind a human, set hard stop conditions, trace each step with OpenTelemetry and evaluate continuously.
MCP for DevOps: Give Agents Pipeline Context Without the Keys
How platform teams can use the Model Context Protocol safely: start with read-only servers and scoped identities behind a gateway, trace every tool call, and add write tools only behind human approval. Includes RBAC, tool and task examples.
Gemini 4 Argon: What It Means for Your Team, and Where to Use It First
Gemini 4 Argon is built to work for hours on one measurable problem. Here is what shipped, the real costs, and how to pilot it safely on your own backlog.
 Balinder Waliaपढ़ें
WSL Vault for Compliance: One Tenant Never Opens Another’s Secrets
How WSL Vault keeps app, team, and environment tenants cryptographically isolated — so a stolen root-style token cannot empty the estate — and why dual-tenant control beats secrets sprawl.
Balinder Waliaपढ़ें 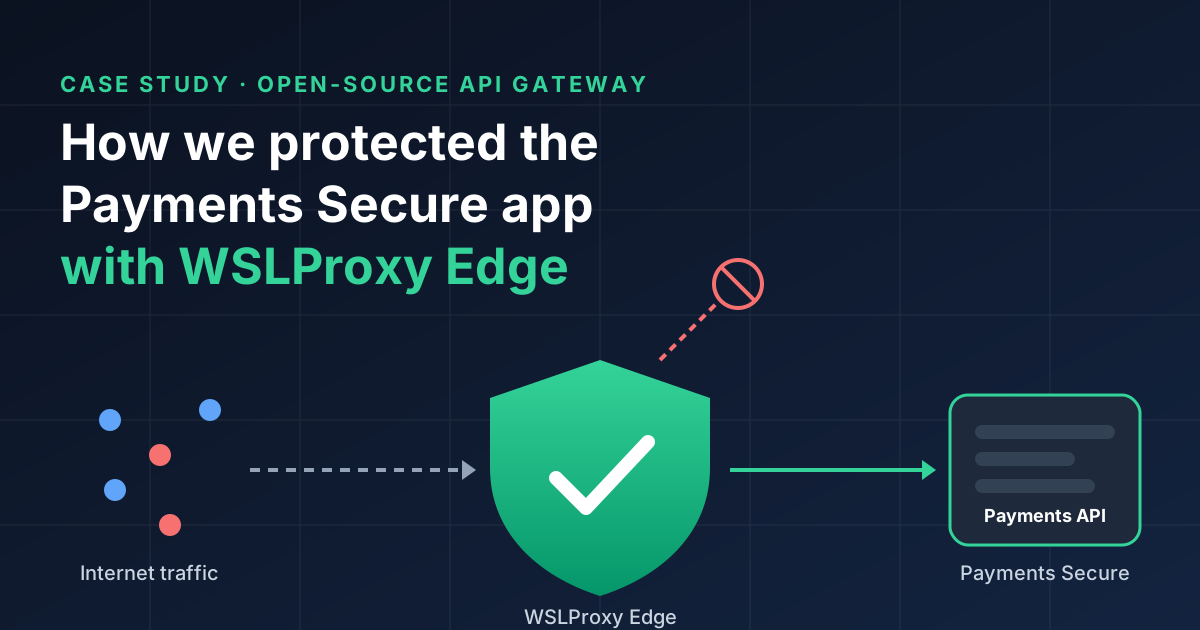
How We Protected the Payments Secure FinTech App with WSLProxy Edge, an Open-Source API Gateway
How we put WSLProxy Edge, our open-source API gateway, in front of Payments Secure (payments-secure.fictionally.org): real-IP checks, scanner detection, login throttling and audit logs, rolled out safely in audit mode.
Balinder Waliaपढ़ें 
WSLVault: Why AI Agents Need Cryptographic Secrets Isolation
AI agents use secrets at machine speed across tools and tenants. WSLVault seals per tenant so a shared platform never leaks another team's plaintext.
Balinder Waliaपढ़ें 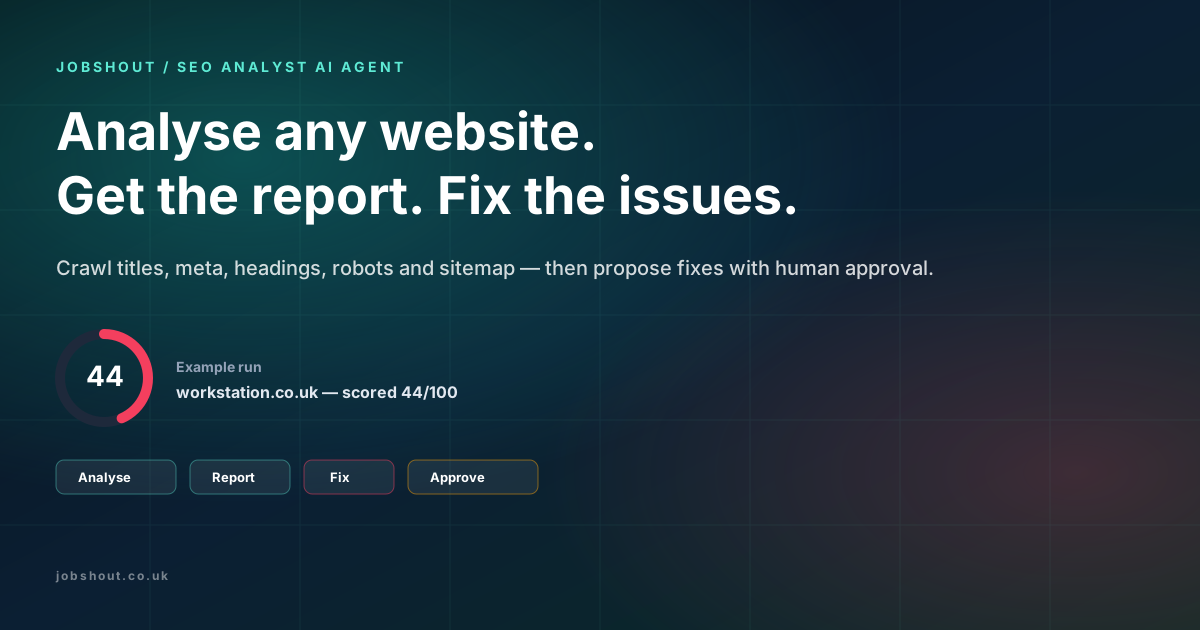
Jobshout SEO Analyst AI Agent — Analyse Any Website & Fix SEO Issues Automatically
We ran Jobshout SEO Analyst on workstation.co.uk — score 44/100 — with concrete fix prompts for missing H1, truncated title, and oversized meta description.
Balinder Waliaपढ़ें 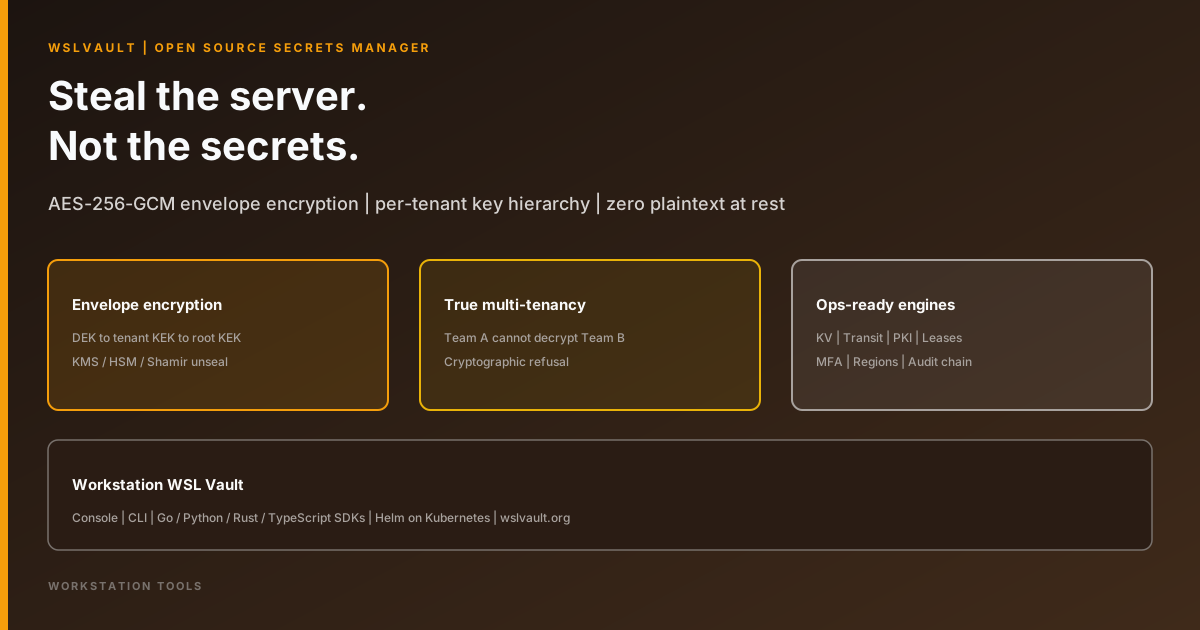
WSLVault: Steal the Server. Not the Secrets.
WSLVault seals secrets before they touch disk — DEK to tenant KEK to root KEK — so a stolen host still leaves attackers with ciphertext they cannot open.
Balinder Waliaपढ़ें