ร้านเปิดให้สั่งแล้ว

เราสร้างเครื่อง Workstation AI สำหรับเว็บไซต์ เอเจนต์ AI และการเทรน LLM — กำหนดค่าและซื้อออนไลน์

ดูราคาสำหรับคู่ค้า
ผลิตภัณฑ์ AI
AI LabsOpenAI AgentsClaude AgentsGrok BotCRM พื้นฐานของ Workstation AIการตลาดผลิตภัณฑ์ทั้งหมด
โซลูชัน AI
AI ประยุกต์เอเจนต์ AIAI เชิงสร้างระบบอัตโนมัติด้วย AIยกระดับทักษะ AIแพ็กเกจ AI สำหรับ SMEห้องปฏิบัติการ AI สำหรับองค์กรเวิร์กสเตชัน AIฮาร์ดแวร์และซอฟต์แวร์ NVIDIANVIDIA Accelerated ComputingAI ส่วนตัวคลัสเตอร์ GPUEdge AIAI ตามอุตสาหกรรม
บริการ AI
ปรับปรุงแพลตฟอร์มให้ทันสมัยวิศวกรรมดิจิทัลรากฐานข้อมูลและ AIการปฏิบัติงานอัตโนมัติที่ปรึกษา AIระบบอัตโนมัติ DevOpsความมั่นคงปลอดภัยไซเบอร์การพัฒนาซอฟต์แวร์การสร้างเอเจนต์การตั้งค่า MLOpsการเช่า GPU
เกี่ยวกับเรา
บริษัทเรื่องราวของเราพันธมิตรเรื่องราวของลูกค้า
ศูนย์ข้อมูล AI
ข้อมูลเชิงลึก AIชุด Jevแล็บเบนช์มาร์กการเลือกโมเดล
บันทึกทางเทคนิค
เอกสารประกอบ
ระบบปฏิบัติการ LinuxUbuntuRed Hat Enterprise LinuxSUSE LinuxAlpine LinuxDebian, Rocky & AlmaLinux
แพลตฟอร์มคลาวด์ AIAWS & Amazon BedrockGoogle Cloud & Vertex AIMicrosoft Azure & AI Foundryคลาวด์และมาร์เก็ตเพลส GPU
ศูนย์ข้อมูล AI ส่วนตัวสำหรับสำนักงานกฎหมายสำหรับสำนักงานบัญชีแพลตฟอร์มภายในองค์กรคลาวด์ที่ปลอดภัยเต็มรูปแบบ
เครื่องมือRing PromoterJobshout
ข่าวสาร
บล็อก
ติดต่อเราลงชื่อเข้าใช้

เวิร์กสเตชัน AI ซอฟต์แวร์มัลติเอเจนต์ AI โครงสร้างพื้นฐาน GPU และโซลูชันเอเจนต์อัจฉริยะสำหรับธุรกิจยุคใหม่

ติดต่อเรา

โซลูชัน AI

AI ประยุกต์เอเจนต์ AIAI เชิงสร้างระบบอัตโนมัติด้วย AIยกระดับทักษะ AIแพ็กเกจ AI สำหรับ SMEห้องปฏิบัติการ AI สำหรับองค์กรAI ตามอุตสาหกรรม

ผลิตภัณฑ์

ผลิตภัณฑ์ทั้งหมดWorkstation AI native CRM และ ERPการตลาดOpenAI AgentsRing PromoterJobshout

บริษัท

เกี่ยวกับเราบริษัทศูนย์ข้อมูล AIทำไมต้อง Workstationพันธมิตรเรื่องราวของลูกค้าราคาติดต่อTenthMatrix

แหล่งข้อมูล

ข้อมูลเชิงลึก AIบันทึกทางเทคนิคเอกสารประกอบระบบปฏิบัติการ Linuxแพลตฟอร์มคลาวด์ AIศูนย์ข้อมูล AI ส่วนตัวบล็อกค้นหาแผนผังเว็บไซต์
สำนักงานสหราชอาณาจักร
77-79 Marlowes, Hemel Hempstead HP1 1LFเส้นทาง - ออกทางแยกที่ 20 จาก M25 Outer Londonเลขทะเบียนบริษัท: 11641870จ. - ศ.: 9:00 - 18:00 น. GMT
+44 7515 356 146
สำนักงานเบลเยียม
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683จ. - ศ.: 9:00 - 18:00 น. CET
+32 492 45 67 46
สำนักงานอินเดีย
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI สงวนลิขสิทธิ์

ความเป็นส่วนตัวการลบข้อมูลคุกกี้ข้อกำหนดในการให้บริการแผนผังเว็บไซต์

NVIDIA, the NVIDIA logo, RTX, RTX PRO, Blackwell, CUDA, NVLink, MGX, Omniverse, Spectrum-X, Quantum, BlueField, DGX and HGX are trademarks and/or registered trademarks of NVIDIA Corporation in the US and other countries. AMD, the AMD Arrow logo, EPYC, Instinct, Ryzen and Threadripper are trademarks of Advanced Micro Devices, Inc. Dell and PowerEdge are trademarks of Dell Inc. or its subsidiaries. Intel and Xeon are trademarks of Intel Corporation or its subsidiaries. AMAX, AceleMax and LiquidMax are trademarks of AMAX Engineering Corporation. All other product names, logos and brands are the property of their respective owners. We use them only to identify the products we describe, supply or support; their use does not mean their owners endorse us.

หน้าแรก / บันทึกทางเทคนิค / Technology
DevOpsSecuritySREKubernetes

WSLVault: Steal the Server. Not the Secrets.

Technical brief: AES-256-GCM envelope hierarchy, cryptographic tenant isolation, engines, identity/MFA, active/active regions, Kubernetes deploy, and video chapters

22 กันยายน 2569Technology3 min read

This is the long-form deep dive companion to the intro blog. Product page: Workstation WSL Vault · wslvault.org · GitHub.
WSLVault — steal the server, not the secrets

20-minute intro — youtu.be/O6q3_H0k2M8

Thesis. Secrets management fails closed only when ciphertext at rest is worthless without key custody. WSLVault wraps every secret under a per-tenant hierarchy (DEK → tenant KEK → root KEK) so a stolen server, disk, or database dump does not equal stolen secrets.

1. Why this matters — steal the server

Classic failure mode: back up a database, lose a laptop, or compromise a host — and the attacker leaves with readable credentials. “Encryption at rest” that shares one key across every tenant, or that stores unwrapped material beside ciphertext, collapses under that scenario.

WSLVault’s design answer is simple to state and hard to fake: seal secrets before they touch disk, isolate tenants at the key layer, and keep root custody outside the data plane (KMS, HSM, or Shamir quorum).

2. What WSLVault is

WSLVault is an open-source, self-hosted secrets manager with Vault-compatible workflows:

  • Versioned KV secrets
  • Transit encryption (encrypt / decrypt / sign / verify)
  • PKI and short-lived certificates
  • Dynamic leases with real revoke
  • Identity, policies, and MFA
  • Active/active multi-region replication
  • Tamper-evident, hash-chained audit

Operators drive it from a web console, CLI, Go/Python/Rust/TypeScript SDKs, or MCP. Deploy with Helm/GitOps on Kubernetes. Product home: https://www.wslvault.org/.

3. Envelope encryption and key hierarchy
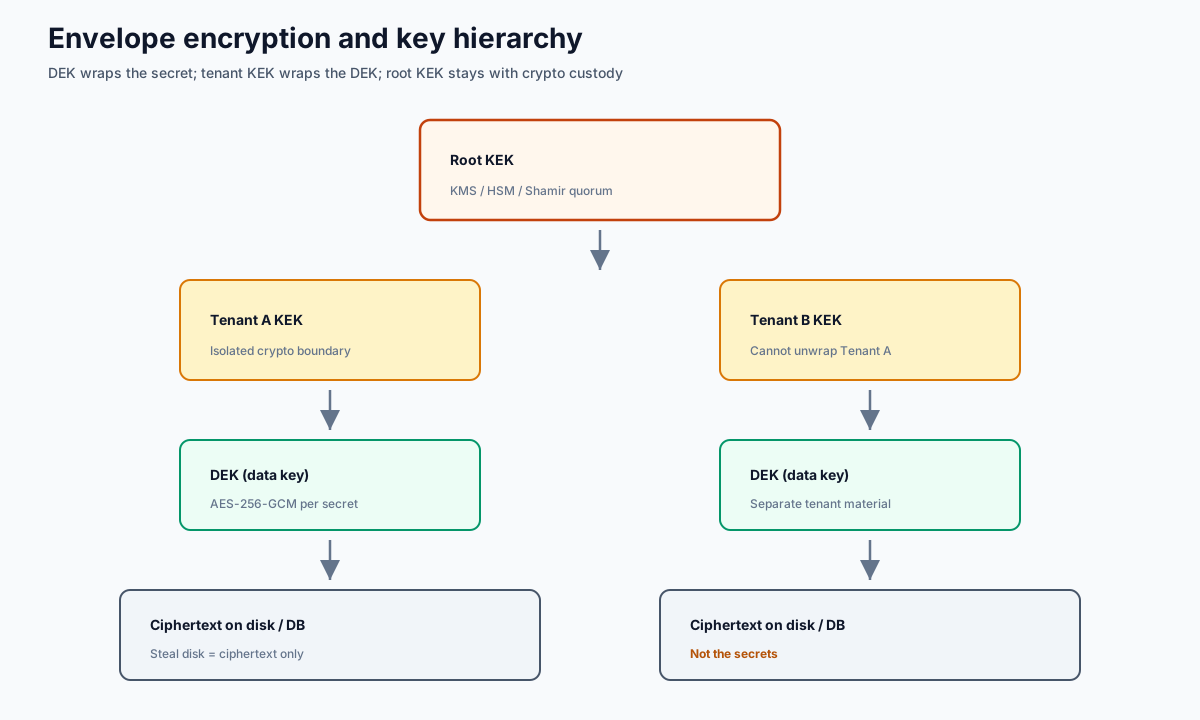
WSLVault envelope encryption hierarchy

Each secret is sealed with a data encryption key (DEK). The DEK is wrapped under a tenant KEK. Tenant KEKs are wrapped under a root KEK held by the crypto service — typically backed by KMS, HSM, or Shamir-split custody so no single operator can unseal alone.

AES-256-GCM provides authenticated encryption. A database dump yields ciphertext wrapped under keys the database never sees. That is the practical meaning of steal the server, not the secrets.

4. Multi-tenancy that actually isolates

Application “tenant IDs” are not enough. In WSLVault, a data key belongs to exactly one tenant. A cross-tenant request returns “not found” rather than another tenant’s data. Isolation holds at the crypto service — Team A cannot decrypt Team B even if a bug in an upper layer misroutes an identifier.

That is cryptographic refusal, not an “oops” in a filter.

5. Console surfaces: secrets, transit, PKI

The steel/brass console walks the same engines as the API:

Engine What operators get
KV v2Versioned reads/writes, check-and-set, soft-delete/destroy, per-path metadata — sealed before storage
TransitEncrypt/decrypt/sign/verify without plaintext keys leaving the vault; rotate while old ciphertext stays readable
PKIPrivate CA, roles, short-lived certs; CA private keys envelope-encrypted under their own root

6. Identity, policies, leases, and MFA

Identity comes from a signed, per-tenant token — never a trusted header alone. Operators get self-service TOTP two-factor with recovery codes, fine-grained policies on API keys and JWTs, plus SCIM, LDAP, OIDC, mTLS, and cloud-workload auth patterns.

Dynamic credentials are leases: issued, listed, renewed, and revoked for real. Revoking a token stops it working immediately — not just flipping a row that something might ignore.

7. Regions, HA, and audit
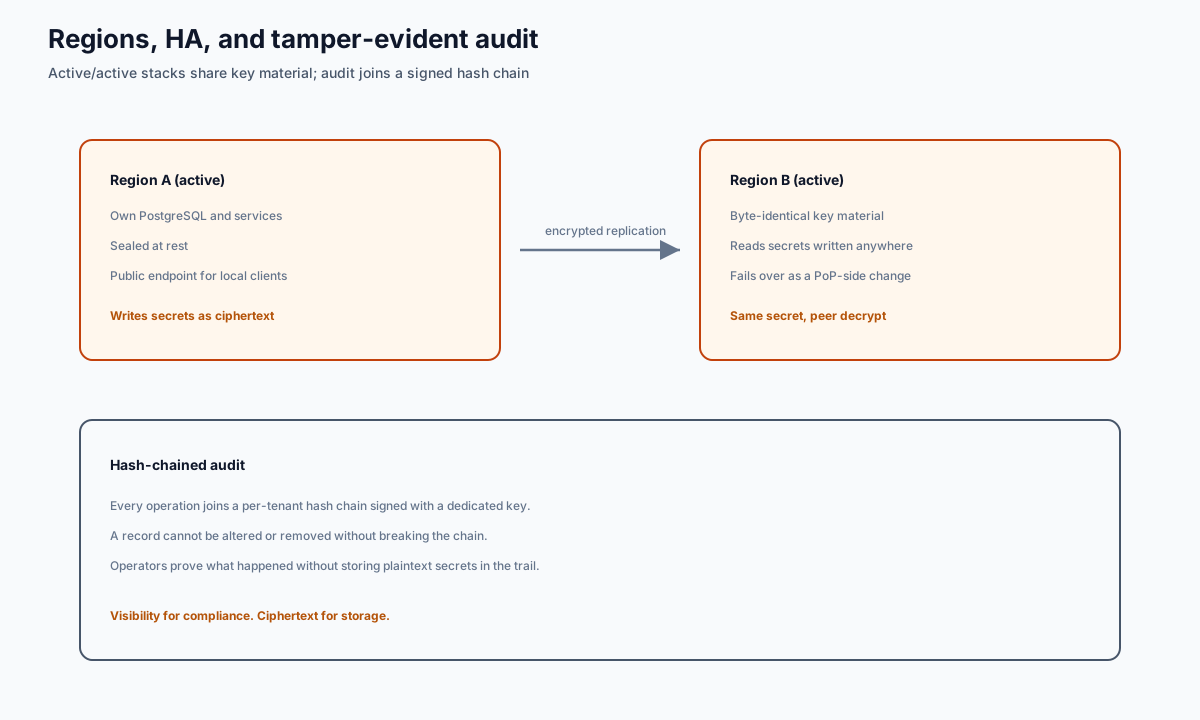
WSLVault multi-region replication and audit

Each region is a complete stack — its own database, services, and public hostname. Regions share key material, not a single live database. Replication moves encrypted changes so a peer can decrypt what was written elsewhere.

Every operation joins a per-tenant hash chain signed with a dedicated key. A record cannot be altered or removed without breaking the chain. That gives compliance visibility without storing plaintext secrets in the trail.

8. Deploy on Kubernetes

Ship with the Helm chart and Kubernetes operator, drive from GitOps, scrape with Prometheus, and reach the vault from SDKs or an AI agent over the built-in MCP server. Start from the official guide: GETTING-STARTED.md.

9. Video chapters

Time Topic
0:00Why this matters (steal the server)
1:30What WSLVault is
3:00Envelope encryption and key hierarchy
5:30Multi-tenancy that actually isolates
8:00Console walkthrough (secrets, transit, PKI)
11:00Identity, policies, leases and MFA
14:00Regions, HA and audit
17:00Deploy on Kubernetes
19:00Where to go next

10. Where to go next

  • Product: /en/wsl-vault
  • Site: wslvault.org
  • Repo: github.com/bwalia/wslvault
  • Docs: docs/
  • Related Workstation tools: WSL Proxy, Ring Promoter

Published by Workstation.

แชร์บทความนี้

เพิ่มเติมใน Technology

AI Is a Five-Layer Cake: What AI Is, How It Works and Why Every Layer Matters

AI Is a Five-Layer Cake: What AI Is, How It Works and Why Every Layer Matters

Jensen Huang's framework explained: energy, chips, infrastructure, models and applications, how each layer depends on the ones below, and what it means for your business.

อ่านต่อ
Jensen Huang on Building the Dynamo of the Intelligence Age: AI Factories, Tokens and Jobs

Jensen Huang on Building the Dynamo of the Intelligence Age: AI Factories, Tokens and Jobs

Notes on NVIDIA founder Jensen Huang's Sequoia Capital interview: why computing is moving from retrieval to generation, why AI factories are this era's dynamos, and why AI changes tasks rather than erasing jobs.

อ่านต่อ
Installing the NVIDIA Container Toolkit: Docker, containerd, CRI-O, Podman and Kubernetes

Installing the NVIDIA Container Toolkit: Docker, containerd, CRI-O, Podman and Kubernetes

Install the toolkit with apt, dnf or zypper, configure every container engine, use CDI, test GPU access, and fix the errors you will meet, with advice for running it across a fleet.

อ่านต่อ

