NGINX Vulnerabilities: Protecting Your Infrastructure

NGINX sits in front of most modern web properties. NGINX is the world's most widely used open-source web server [1]. For teams in manufacturing, supermarkets, banking, education, HealthTech, FinTech and tax returns, that front door is often the only thing between the public internet and critical applications: shop floor dashboards, point-of-sale APIs, online banking portals, student records, patient data exchanges, payment processing and tax filing services.
When that front door is vulnerable, the impact is sector-specific and immediate.
Understanding the Implications of Nginx Vulnerabilities
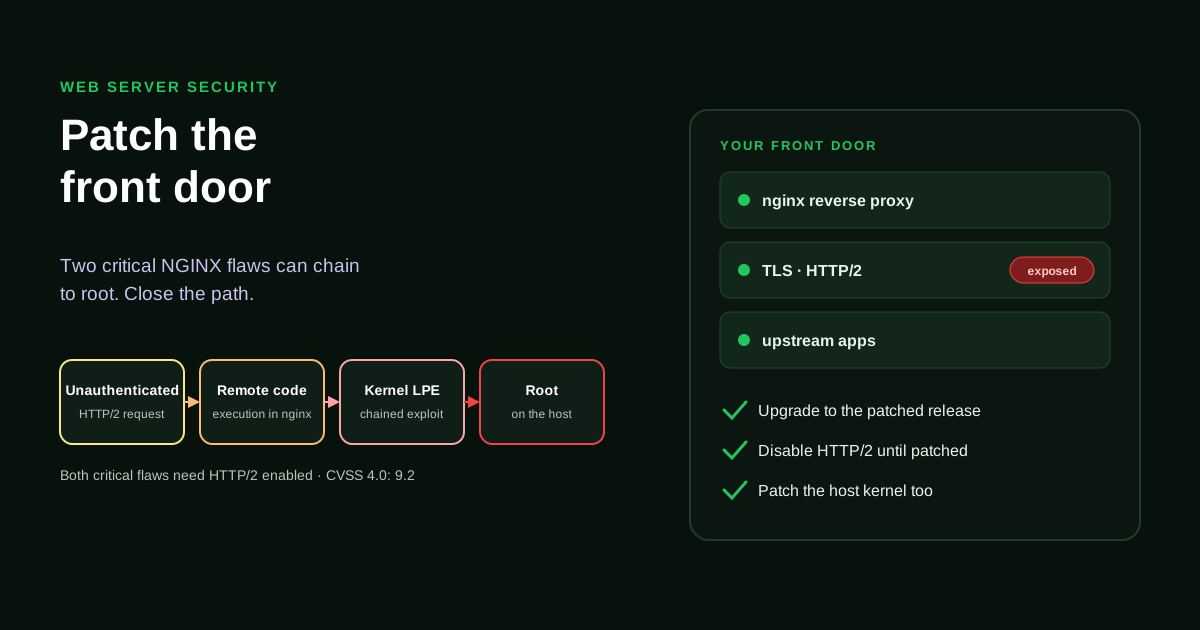
Two recent flaws, tracked as CVE-2026-123633 and CVE-2026-123007, are both rated Critical, with a CVSS 4.0 score of 9.2 [1]. Both vulnerabilities require HTTP/2 to be enabled on the affected NGINX server [1].
The worst NGINX vulnerability would allow an unauthenticated attacker to execute commands on an affected nginx server with HTTP/2 enabled [2]. That is remote code execution without credentials.
If chained with the NGINX vulnerability, the LPE kernel vulnerability would allow an attacker to gain root privileges on the host [2].
CVE-2026-123007 affects versions dating back to NGINX 1.9.5 in 2015 [1]. In practice this means long-running infrastructure in manufacturing and education — where a stable release has been in place for years — is in scope.
For supermarkets, an exploited edge NGINX can take down self-checkout APIs or inventory systems during peak hours. For banking and FinTech, the same flaw can expose customer-facing login and transaction endpoints. In HealthTech, an unauthenticated RCE on a reverse proxy in front of FHIR APIs risks PHI exposure and regulatory breach. In tax returns, the window around filing season makes availability loss as damaging as data loss.
The common thread is not the technology; it is the role NGINX plays as a shared, internet-facing router for business-critical services.
Protecting Against CVE-2026-123633 and CVE-2026-123007
Mitigation starts with exposure reduction and patching.
Reduce attack surface immediately
Confirm whether HTTP/2 is enabled and whether it is required. Both vulnerabilities require HTTP/2 to be enabled on the affected NGINX server [1]. If HTTP/2 can be disabled temporarily while you patch, that removes the attack surface immediately.
Patch
Upgrade to a fixed NGINX build as soon as it is available for your distribution. For CVE-2026-123007, the long history of affected versions means many environments will need a deliberate upgrade plan rather than an in-place patch [1].
Compensating controls at the edge
Apply controls while patching is staged. Limiting the number of simultaneous connections can prevent abuse of the server [3]. Setting large_client_header_buffers to 2 1k can help combat bad bots and DoS attacks [3].
These controls do not replace a patch, but they reduce the ability of an attacker to probe and amplify the flaw while you coordinate a maintenance window.
A practical prioritization table for teams with limited change windows:
| Control | What it does | When to use | Limitation |
|---|---|---|---|
| Disable HTTP/2 | Removes requirement for both CVEs | Emergency, if clients tolerate HTTP/1.1 | Breaks HTTP/2-only clients |
| Patch NGINX | Fixes root cause | As soon as tested build is available | Requires restart, testing |
| Limit connections | Thwarts brute force / connection exhaustion | Always, with tuned limits | Does not stop a single crafted request |
| Reduce header buffers | Mitigates header abuse and DoS | Always for internet-facing | May break clients with large headers |
Use Disable HTTP/2 as an emergency stopgap, Patch NGINX as the definitive fix, and keep Limit connections and Reduce header buffers as ongoing hardening. The table prioritizes by risk reduction per change risk.
Setting Up Nginx Configuration for Security
Security configuration is a set of layered directives, not a single switch.
Start by auditing the current config. Look for listen 443 ssl http2; and any proxy pass rules that expose internal services. Document which sites actually need HTTP/2.
Next, harden the request parsing surface. Large or malformed headers are a common amplification vector.
Example snippet for an internet-facing server:
http {
  # Connection limiting per IP
  limit_conn_zone $binary_remote_addr zone=slimits:10m;

  # Header buffer hardening
  large_client_header_buffers 2 1k;

  server {
  listen 443 ssl http2;
  server_name api.example.com;

  limit_conn slimits 5;

  client_max_body_size 1m;
  client_header_timeout 10s;
  client_body_timeout 10s;

  location / {
  proxy_pass http://app_upstream;
  proxy_set_header Host $host;
  }
  }
}
large_client_header_buffers 2 1k sets the maximum number and size of buffers for large headers to read from client request. This is the directive referenced for combating bad bots and DoS attacks [3]. limit_conn slimits 5; limits remote clients to no more than 5 concurrently open connections per remote IP address. Limiting the number of simultaneous connections can prevent abuse of the server [3].
Test the snippet in staging with production-like traffic before promoting. Manufacturing devices and older educational systems sometimes send large headers with legacy authentication tokens.
Limiting Simultaneous Connections and Large Client Header Buffers
Connection limits and header buffer limits address different abuse patterns.
Connection limiting protects availability. In supermarkets, a runaway POS sync or a botnet can exhaust worker connections and starve legitimate checkouts. In banking, connection exhaustion can deny access to mobile banking during market hours. A per-IP limit of 5-10 concurrent connections is a reasonable starting point for public APIs, tuned by baseline metrics.
Header buffer limits protect parsing. Setting large_client_header_buffers to 2 1k can help combat bad bots and DoS attacks [3]. Smaller buffers cause NGINX to reject oversized headers early instead of allocating excessive memory.
The trade-off is client compatibility. Test with production traffic captures before enforcing tight limits.
Version exposure overview:
| Vulnerability | CVSS 4.0 | HTTP/2 required | First affected version |
|---|---|---|---|
| CVE-2026-123633 | 9.2 Critical [1] | Yes [1] | Not specified in sources |
| CVE-2026-123007 | 9.2 Critical [1] | Yes [1] | NGINX 1.9.5 in 2015 [1] |
Best Practices for Nginx Security
Patch cadence matters more than any single directive. Maintain an inventory of NGINX instances, including those in DMZ, internal API gateways and container sidecars. For HealthTech and FinTech, map each instance to data classification and regulatory scope.
Segment and monitor. Place NGINX behind a WAF or API gateway where possible, and log HTTP/2 error codes and connection drops. Alert on spikes in 400/502 responses and on connection limit rejections.
Test changes in a staging environment that mirrors production traffic patterns. Tax return platforms see seasonal spikes; education platforms see spikes at term start. Validate limits under load.
Document the rollback plan. If disabling HTTP/2 or tightening header buffers causes client failures, you need a one-command revert.
Finally, treat NGINX as infrastructure, not just software. The worst flaw, it says, would allow an unauthenticated attacker to execute commands on an affected nginx server with HTTP/2 enabled [2]. In manufacturing and supermarkets, that means operational technology visibility. In banking, HealthTech, FinTech and tax, it means regulated data exposure.
A disciplined patch window, reduced attack surface via HTTP/2 controls, and connection and header hardening together reduce risk while you move to a fully fixed fleet.
References
- Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 — wiz.io
- NGINX2Root: Remote Code Execution vulnerabilities in nginx — lwn.net
- Top 25 Nginx Web Server Best Security Practices — cyberciti.biz (6 March 2010)