شاپ کھل گئی ہے

ہم ویب سائٹس، AI ایجنٹس اور LLM ٹریننگ کے لیے Workstation AI مشینیں بناتے ہیں — آن لائن ترتیب دیں اور خریدیں۔

ٹریڈ قیمتیں حاصل کریں
AI مصنوعات
AI لیبزOpenAI ایجنٹسClaude ایجنٹسGrok BotWorkstation AI نیٹو CRMمارکیٹنگتمام مصنوعات
AI حل
اطلاقی AIAI ایجنٹسجنریٹو AIAI آٹومیشنAI مہارت میں اضافہSME کے لیے AI پیکجزانٹرپرائز AI لیبAI ورک سٹیشنزNVIDIA ہارڈویئر اور سافٹ ویئرNVIDIA ایکسلریٹڈ کمپیوٹنگپرائیویٹ AIGPU کلسٹرزایج AIصنعت کے لحاظ سے AI
AI خدمات
پلیٹ فارم کی جدید کاریڈیجیٹل انجینئرنگڈیٹا کی بنیاد اور AIخودمختار آپریشنزAI مشاورتDevOps آٹومیشنسائبر سیکیورٹیسافٹ ویئر ڈیولپمنٹایجنٹ بلڈنگMLOps سیٹ اپGPU لیزنگ
ہمارے بارے میں
کمپنیہماری کہانیشراکت دارکسٹمر کہانیاں
AI ڈیٹا سینٹرز
AI بصیرتیںJev سلسلہبینچ مارک لیبماڈل کا انتخاب
تکنیکی نوٹس
دستاویزات
Linux OSUbuntuRed Hat Enterprise LinuxSUSE LinuxAlpine LinuxDebian, Rocky & AlmaLinux
AI کلاؤڈ پلیٹ فارمزAWS & Amazon BedrockGoogle Cloud & Vertex AIMicrosoft Azure & AI FoundryGPU کلاؤڈز اور مارکیٹ پلیسز
نجی AI ڈیٹا سینٹرزقانونی فرموں کے لیےاکاؤنٹنگ فرموں کے لیےآن پریمیسز پلیٹ فارمزمکمل محفوظ کلاؤڈ
ٹولزRing PromoterJobshout
خبریں
بلاگ
ہم سے رابطہ کریںسائن ان

جدید کاروبار کے لیے AI ورک اسٹیشنز، AI ملٹی ایجنٹک سافٹ ویئر، GPU انفراسٹرکچر اور ذہین ایجنٹ حل۔

ہم سے رابطہ کریں

AI حل

اطلاقی AIAI ایجنٹسجنریٹو AIAI آٹومیشنAI مہارت میں اضافہSME کے لیے AI پیکجزانٹرپرائز AI لیبصنعت کے لحاظ سے AI

مصنوعات

تمام مصنوعاتWorkstation AI native CRM اور ERPمارکیٹنگOpenAI ایجنٹسRing PromoterJobshout

کمپنی

ہمارے بارے میںکمپنیAI ڈیٹا سینٹرزWorkstation کیوںشراکت دارکسٹمر کہانیاںقیمتیںرابطہTenthMatrix

وسائل

AI بصیرتیںتکنیکی نوٹسدستاویزاتLinux OSAI کلاؤڈ پلیٹ فارمزنجی AI ڈیٹا سینٹرزبلاگتلاشسائٹ کا نقشہ
برطانیہ کا دفتر
77-79 Marlowes, Hemel Hempstead HP1 1LFراستہ - M25 آؤٹر لندن سے جنکشن 20 لیںکمپنی نمبر: 11641870پیر - جمعہ: صبح 9:00 - شام 6:00 GMT
+44 7515 356 146
بیلجیم کا دفتر
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683پیر - جمعہ: صبح 9:00 - شام 6:00 CET
+32 492 45 67 46
بھارت کا دفتر
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI۔ جملہ حقوق محفوظ ہیں۔

رازداریڈیٹا حذف کرناکوکیزسروس کی شرائطویب سائٹ سائٹ میپ

NVIDIA, the NVIDIA logo, RTX, RTX PRO, Blackwell, CUDA, NVLink, MGX, Omniverse, Spectrum-X, Quantum, BlueField, DGX and HGX are trademarks and/or registered trademarks of NVIDIA Corporation in the US and other countries. AMD, the AMD Arrow logo, EPYC, Instinct, Ryzen and Threadripper are trademarks of Advanced Micro Devices, Inc. Dell and PowerEdge are trademarks of Dell Inc. or its subsidiaries. Intel and Xeon are trademarks of Intel Corporation or its subsidiaries. AMAX, AceleMax and LiquidMax are trademarks of AMAX Engineering Corporation. All other product names, logos and brands are the property of their respective owners. We use them only to identify the products we describe, supply or support; their use does not mean their owners endorse us.

ہوم / تکنیکی نوٹس / Technology
DevOpsSecurityAISRE

WSLVault: Why AI Agents Need Cryptographic Secrets Isolation

Technical brief: why agentic systems raise the stakes for secret lifecycle, cosmetic tenant filters vs cryptographic refusal, envelope keys, leases, and video chapters

24 ستمبر، 2026Technology4 min read

Long-form companion to the blog. For platform and security architects shipping AI agents on shared infrastructure: why secret lifecycle is non-negotiable, and why isolation must be cryptographic — not a WHERE clause. Product: Workstation WSL Vault · wslvault.org · GitHub.
WSLVault — AI agents and cryptographic secrets isolation

~20 min — youtu.be/O6q3_H0k2M8 · same recording angled for tenancy

Thesis. AI agents amplify every secrets mistake: they call tools at machine speed, keep credentials across loops, and often share multi-tenant platforms. Protecting, rotating, and managing secrets is therefore more critical for agents than for classic services — and isolation that depends only on application filters is not isolation.

1. Why protecting, rotating, and managing secrets is even more critical for AI agents

Classic apps usually fetch a small set of credentials at startup. Agents are different:

  • Tool sprawl — one session may need cloud APIs, databases, ticketing, email, and MCP servers. Each credential is a live capability, not a config value.
  • Session persistence — keys sitting in env files, chat context, or MCP configs outlive a single request. Without rotation and leases, compromise windows stay open.
  • Autonomous action — once an agent holds a token, it will use it. There is no “wait for the human to notice” between leak and abuse.
  • Multi-tenant agent platforms — Team A’s agent and Team B’s agent may share schedulers, storage, and observability. A bug or a stolen database dump must never hand one tenant the other’s plaintext.
  • Compliance and audit — regulators and customers ask who accessed which secret, for which agent, and whether the trail can be tampered with.

That is why the control set for agents is stricter: protect (envelope encryption at rest), rotate (KEK/DEK and static roles on a period), and manage (identity-bound policies, short-lived leases, real revoke).

Agent digest. (1) Never put long-lived secrets in agent prompts or MCP config files. (2) Issue dynamic credentials with TTL; renew near expiry; revoke on stop. (3) Bind identity per tenant and per agent workload. (4) Assume shared infrastructure — require cryptographic tenant isolation, not cosmetic tenant IDs.

2. Why tenant IDs alone are cosmetic isolation

Most “multi-tenant vaults” isolate with application filters: WHERE tenant_id = ?. That fails closed only if every code path is perfect forever — including backups, analytics jobs, support tools, and the next junior PR.

When Team A and Team B share a platform, ask: can a bug or a stolen database dump ever hand one team the other’s plaintext? If the answer depends on a filter, the answer is yes.
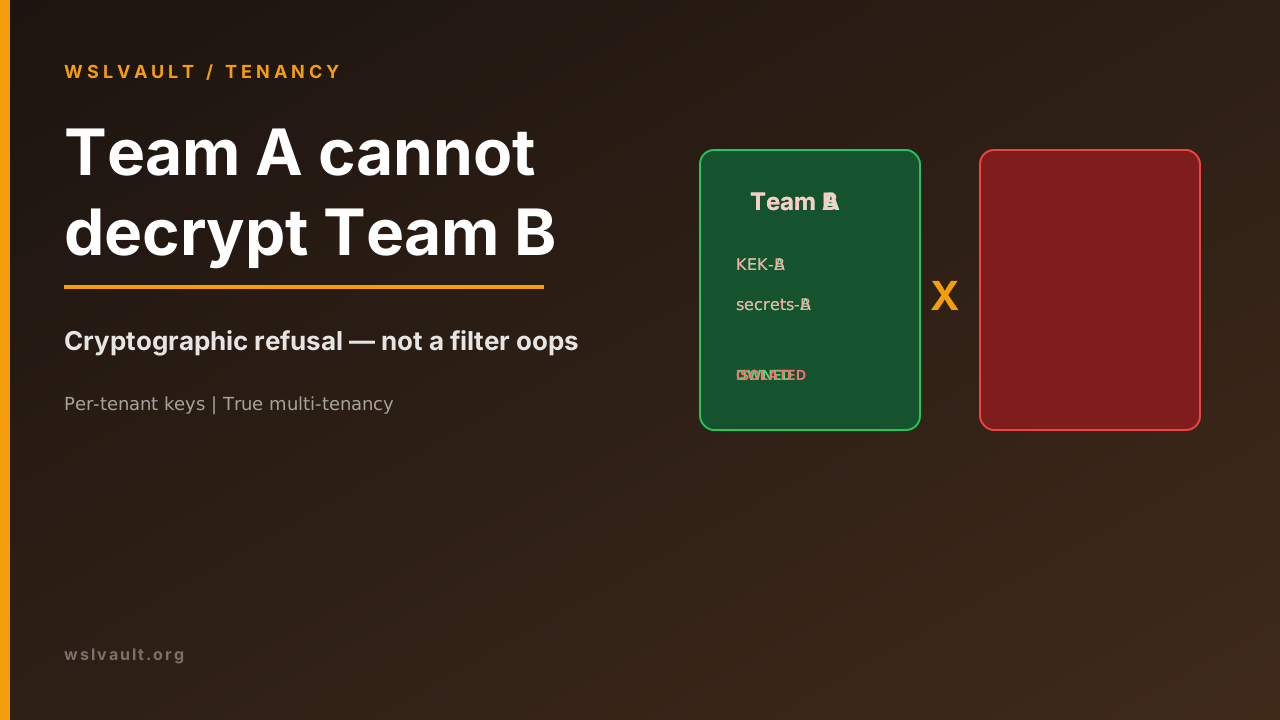
Team A cannot decrypt Team B

3. Cryptographic refusal — WSLVault’s answer

WSLVault seals every secret before storage under a per-tenant hierarchy: DEK → tenant KEK → root KEK (KMS / HSM / Shamir). Each data key belongs to exactly one tenant. A cross-tenant request returns not found, not another tenant’s row with the wrong label.

That is cryptographic refusal: Team A cannot decrypt Team B even if an upper layer misroutes an identifier. Isolation holds at the crypto service — the place filter bugs cannot quietly rewrite.
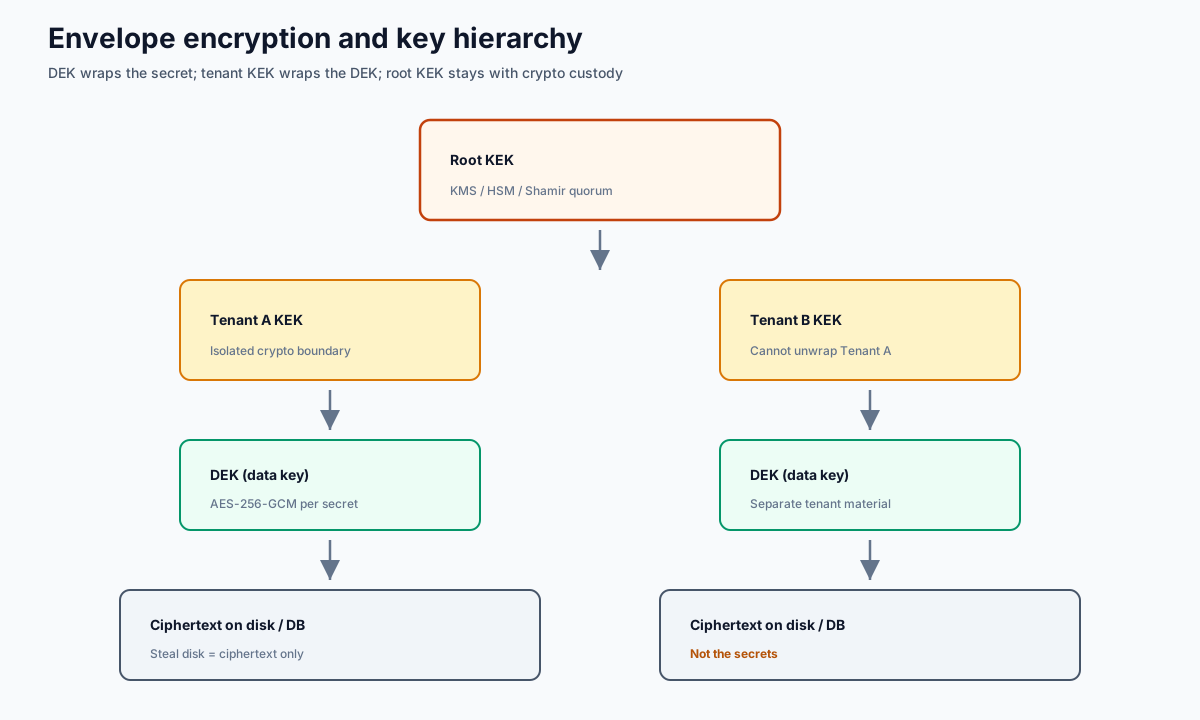
WSLVault envelope encryption key hierarchy

4. Engines still work per tenant

Isolation does not mean you lose Vault-compatible workflows. Per tenant you still get:

Engine Why agents care
KV v2Versioned config and API material sealed before disk — not plaintext beside the agent runtime
TransitEncrypt/decrypt/sign without exporting keys into the model or tool process
PKIShort-lived certs for mTLS between agent, MCP, and backends
LeasesDynamic credentials with renew/revoke — stop the agent, kill the access

5. Protect → rotate → manage (agent checklist)

  1. Protect — envelope encryption; root custody outside the data plane; no plaintext in backups or audit payloads.
  2. Rotate — rotate tenant KEKs and static roles on a period; keep old ciphertext readable via transit versioning where needed.
  3. Manage — identity-bound tokens (not trusted headers alone), fine-grained policies, MFA for operators, leases with real revoke for agent sessions.
  4. Prove — tamper-evident, hash-chained audit per tenant so you can show who did what without storing secrets in the trail.
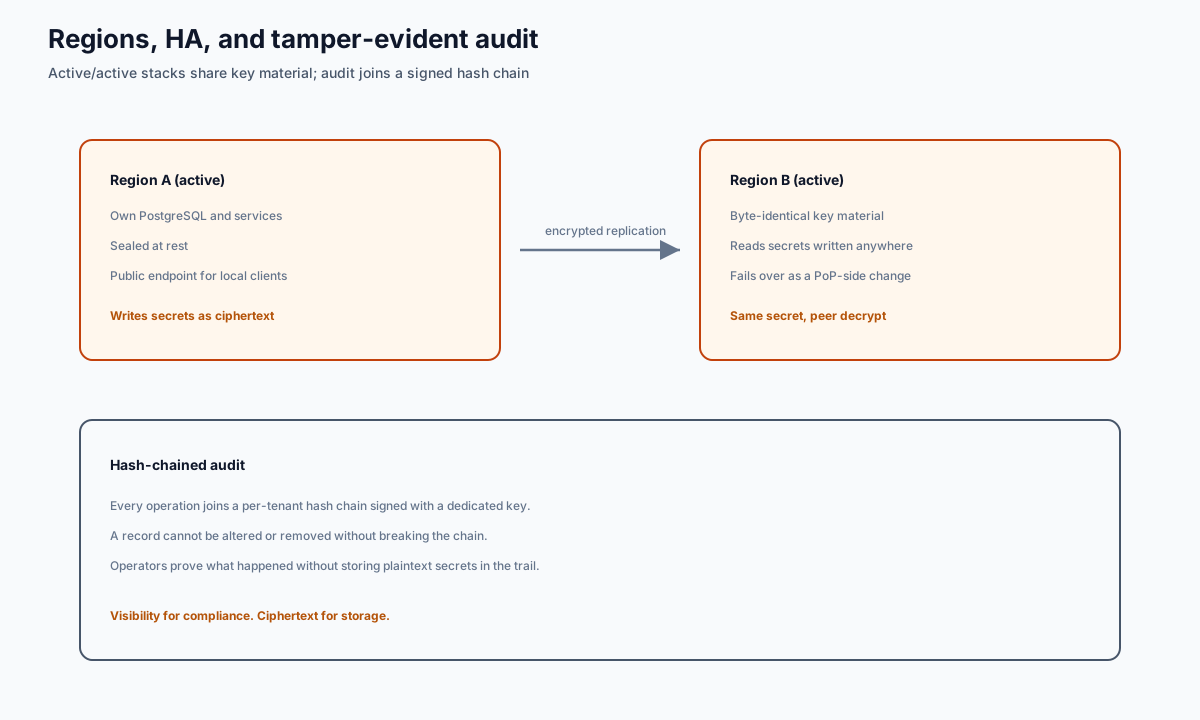
WSLVault multi-region and tamper-evident audit

6. Video chapters

Time Topic
0:00Why this matters (steal the server)
1:30What WSLVault is
3:00Envelope encryption and key hierarchy
5:30Multi-tenancy that actually isolates
8:00Console walkthrough (secrets, transit, PKI)
11:00Identity, policies, leases and MFA
14:00Regions, HA and audit
17:00Deploy on Kubernetes
19:00Where to go next

7. Where to go next

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault
  • Intro brief: Steal the server. Not the secrets.
  • Related: Agentic AI security — MCP, OAuth, Vault leases

Published by Workstation.

یہ مضمون شیئر کریں

Technology میں مزید

AI Is a Five-Layer Cake: What AI Is, How It Works and Why Every Layer Matters

AI Is a Five-Layer Cake: What AI Is, How It Works and Why Every Layer Matters

Jensen Huang's framework explained: energy, chips, infrastructure, models and applications, how each layer depends on the ones below, and what it means for your business.

مزید پڑھیں
Jensen Huang on Building the Dynamo of the Intelligence Age: AI Factories, Tokens and Jobs

Jensen Huang on Building the Dynamo of the Intelligence Age: AI Factories, Tokens and Jobs

Notes on NVIDIA founder Jensen Huang's Sequoia Capital interview: why computing is moving from retrieval to generation, why AI factories are this era's dynamos, and why AI changes tasks rather than erasing jobs.

مزید پڑھیں
Installing the NVIDIA Container Toolkit: Docker, containerd, CRI-O, Podman and Kubernetes

Installing the NVIDIA Container Toolkit: Docker, containerd, CRI-O, Podman and Kubernetes

Install the toolkit with apt, dnf or zypper, configure every container engine, use CDI, test GPU access, and fix the errors you will meet, with advice for running it across a fleet.

مزید پڑھیں

