
WSLVault: Steal the Server. Not the Secrets.
Open-source secrets manager with envelope encryption, true multi-tenancy, KV/transit/PKI/leases, multi-region HA, and hash-chained audit
 Balinder Walia22 ستمبر، 20261 min read
Steal the server. Not the secrets. WSLVault is an open-source, self-hosted secrets manager built on AES-256-GCM envelope encryption and a per-tenant key hierarchy. This intro covers what it is, why the model matters, and how you drive it from console, CLI, or SDKs. Deep dive: long article · Product: /wsl-vault.

Watch on YouTube (~20 min)
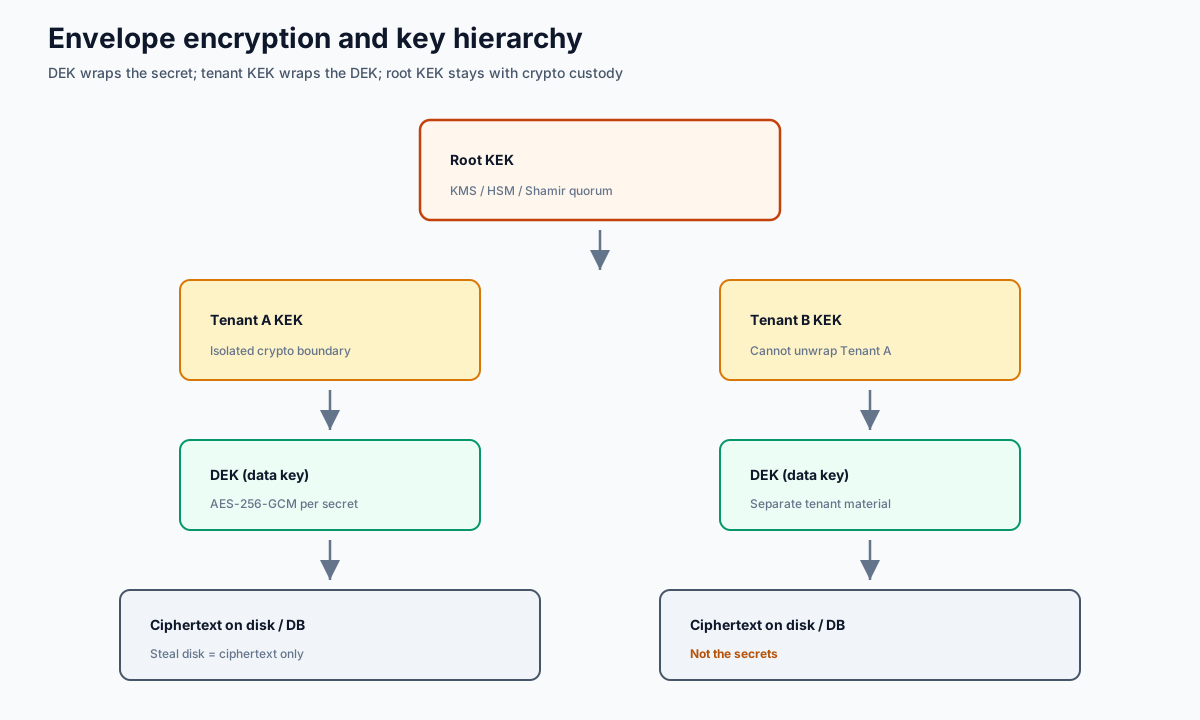
Bottom line. A stolen disk, database dump, or compromised host should leave attackers with ciphertext they cannot open. WSLVault seals every secret before storage — DEK → tenant KEK → root KEK — so multi-tenancy is cryptographic, not cosmetic.
WSLVault is built for operators who want Vault-compatible workflows without plaintext at rest: Rust services, Helm/GitOps on Kubernetes, CLI plus Go/Python/Rust/TypeScript SDKs, and a steel/brass web console.
What you will learn
- True multi-tenancy — Team A cannot decrypt Team B (cryptographic refusal, not “oops”)
- Envelope encryption — DEK → tenant KEK → root KEK (KMS / HSM / Shamir)
- Engines — KV secrets, transit encryption, PKI, dynamic leases, MFA
- Operations — Active/active multi-region replication and tamper-evident, hash-chained audit
- Why it matters — Steal the disk ≠ steal the secrets
Links
- Site: https://www.wslvault.org/
- GitHub: https://github.com/bwalia/wslvault
- Docs: docs/
- Getting started: GETTING-STARTED.md
- Workstation product page: /en/wsl-vault
Read the full technical brief · Open the WSL Vault tools page