Workstation Logo
পণ্য
এআই ল্যাবসOpenAI এজেন্টClaude এজেন্টGrok BotWorkstation CRM (WSL CRM)মার্কেটিংসব পণ্য
এআই সমাধান
এআই ওয়ার্কস্টেশনAI SME Packagesপ্রাইভেট এআইজিপিইউ ক্লাস্টারএজ এআইএন্টারপ্রাইজ এআই ল্যাবশিল্প অনুযায়ী এআই
সেবাসমূহ
Platform ModernisationDigital EngineeringData Foundations & AIAutonomous Operationsএআই পরামর্শDevOps অটোমেশনসাইবার নিরাপত্তাসফটওয়্যার ডেভেলপমেন্টএজেন্ট নির্মাণMLOps সেটআপ
আমাদের সম্পর্কে
অংশীদারগ্রাহক গল্প
প্রবন্ধ
ডকুমেন্টেশন
WSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7
ব্লগ
যোগাযোগ করুনLogin
Workstation

আধুনিক ব্যবসার জন্য AI ওয়ার্কস্টেশন, AI মাল্টি-এজেন্টিক সফটওয়্যার, GPU অবকাঠামো এবং বুদ্ধিমান এজেন্ট সমাধান।

যোগাযোগ করুন

AI সমাধান

এআই ওয়ার্কস্টেশনAI SME Packagesপ্রাইভেট এআইজিপিইউ ক্লাস্টারএজ এআইএন্টারপ্রাইজ এআই ল্যাবশিল্প অনুযায়ী এআই

পণ্য

সব পণ্যWSL CRM ও ERPমার্কেটিংOpenAI এজেন্টWSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7

কোম্পানি

আমাদের সম্পর্কেকেন Workstationঅংশীদারগ্রাহক গল্পমূল্যযোগাযোগ

রিসোর্স

প্রবন্ধডকুমেন্টেশনব্লগখুঁজুনসাইটম্যাপ
যুক্তরাজ্য অফিস
77-79 Marlowes, Hemel Hempstead HP1 1LFদিকনির্দেশ - M25 আউটার লন্ডন থেকে জংশন ২০ নিনকোম্পানি নং: 11641870সোম - শুক্র: সকাল ৯:০০ - সন্ধ্যা ৬:০০ GMT
+44 7515 356 146
বেলজিয়াম অফিস
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683সোম - শুক্র: সকাল ৯:০০ - সন্ধ্যা ৬:০০ CET
+32 492 45 67 46
ভারত অফিস
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI। সর্বস্বত্ব সংরক্ষিত।

গোপনীয়তাকুকিসেবার শর্তাবলীওয়েবসাইট সাইটম্যাপ

Loading blog...

Home / Blog
DevOpsSecuritySREKubernetesAI

WSLVault: Steal the Server. Not the Secrets.

Open-source secrets manager with envelope encryption, true multi-tenancy, KV/transit/PKI/leases, multi-region HA, and hash-chained audit

Balinder Walia২২ সেপ্টেম্বর, ২০২৬1 min read

Steal the server. Not the secrets. WSLVault is an open-source, self-hosted secrets manager built on AES-256-GCM envelope encryption and a per-tenant key hierarchy. This intro covers what it is, why the model matters, and how you drive it from console, CLI, or SDKs. Deep dive: long article · Product: /wsl-vault.

WSLVault — steal the server, not the secrets

Watch on YouTube (~20 min)

Bottom line. A stolen disk, database dump, or compromised host should leave attackers with ciphertext they cannot open. WSLVault seals every secret before storage — DEK → tenant KEK → root KEK — so multi-tenancy is cryptographic, not cosmetic.

WSLVault is built for operators who want Vault-compatible workflows without plaintext at rest: Rust services, Helm/GitOps on Kubernetes, CLI plus Go/Python/Rust/TypeScript SDKs, and a steel/brass web console.

What you will learn

  • True multi-tenancy — Team A cannot decrypt Team B (cryptographic refusal, not “oops”)
  • Envelope encryption — DEK → tenant KEK → root KEK (KMS / HSM / Shamir)
  • Engines — KV secrets, transit encryption, PKI, dynamic leases, MFA
  • Operations — Active/active multi-region replication and tamper-evident, hash-chained audit
  • Why it matters — Steal the disk ≠ steal the secrets
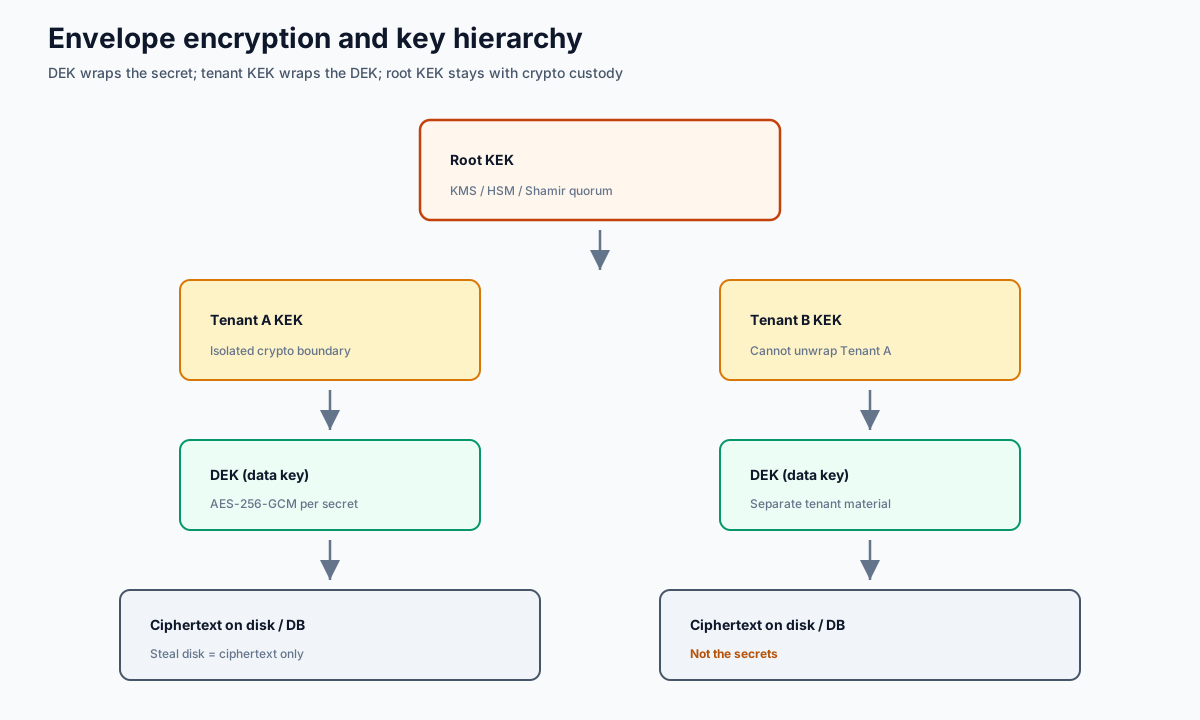
WSLVault envelope encryption key hierarchy

Links

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Docs: docs/
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault

Read the full technical brief · Open the WSL Vault tools page