 Workstation team
At GTC Berlin, Jensen Huang's security film said the only control on many agents today is asking them nicely not to delete files or touch SSH keys. OpenShell is NVIDIA's replacement: a policy, enforced outside the model, on system calls, files and network connections.
What was announced
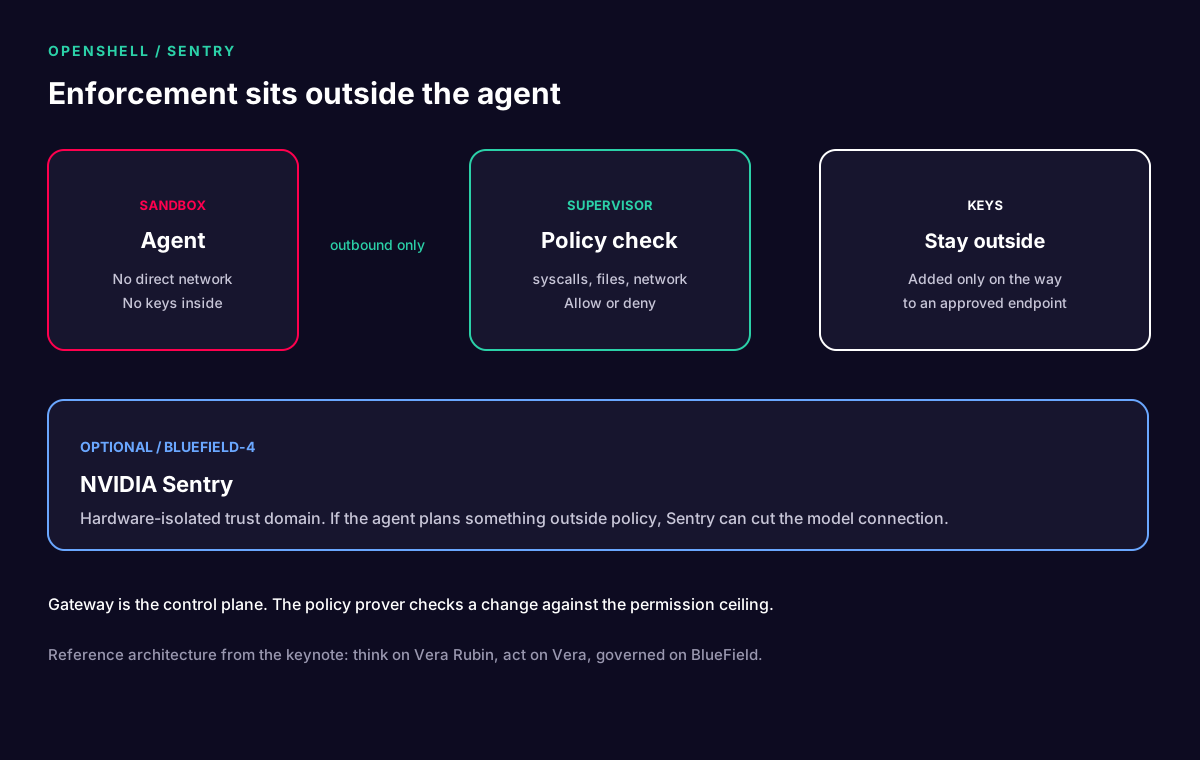
Each agent runs in its own sandbox with no direct network path. Outbound calls go to a supervisor, which allows or denies them. Keys stay outside the sandbox and are attached only on the way to an approved endpoint. A policy change is checked against a permission ceiling so the agent cannot be given more than intended. Sentry, optional, runs on BlueField-4 and can cut the model connection if the agent's plan leaves policy. Huang said that quarantine is in milliseconds. OpenShell is Apache 2.0, and the film said you install a CLI, create a sandbox, and run the agent you already use.
The reference design puts models on Vera Rubin, harnesses on Vera CPUs inside OpenShell, and Sentry on BlueField. Huang's published line: think on Rubin, act on Vera, governed on BlueField. The newsroom list of companies working with that design is long, and NVIDIA marks much of it as when-and-if-available.
The full path, the partner list, and which numbers are NVIDIA's are in the long article. How the CLI sits on a Mac Studio or a Linux GPU box is in our earlier OpenShell operator note.